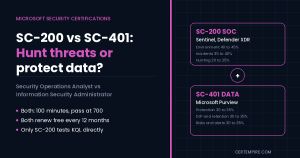
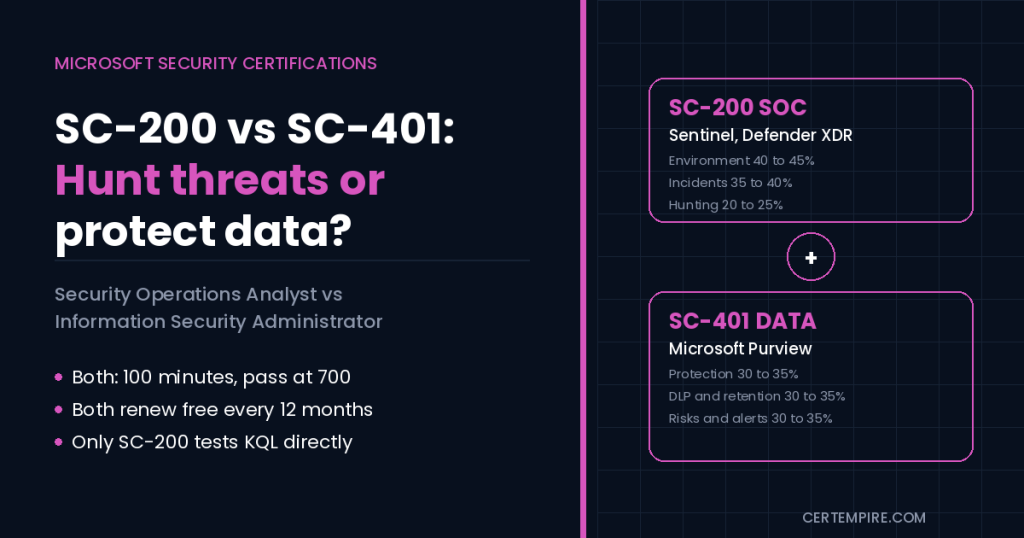
TL;DR: Take SC-200 (Security Operations Analyst) if you want to work in a SOC: triage alerts, investigate incidents in Microsoft Defender XDR and Microsoft Sentinel, and hunt threats with KQL. Take SC-401 (Information Security Administrator) if your job is protecting data: sensitivity labels, data loss prevention, retention, insider risk, and eDiscovery in Microsoft Purview. Both exams run 100 minutes, both pass at 700, and both certifications renew for free every 12 months. Neither shows a retirement notice on Microsoft’s current pages, and both outlines were refreshed in October 2026. The choice comes down to whether you chase threats or govern data.
Quick Facts
| Item | SC-200 | SC-401 |
| Full exam name | Microsoft Security Operations Analyst | Administering Information Security in Microsoft 365 |
| Certification earned | Security Operations Analyst Associate | Information Security Administrator Associate |
| Core role | Triage, incident response, threat hunting, detection engineering | Information protection, DLP, retention, insider risk, audit and eDiscovery |
| Main product | Microsoft Defender XDR and Microsoft Sentinel | Microsoft Purview |
| Exam length | 100 minutes | 100 minutes |
| Passing score | 700 or greater | 700 or greater |
| Question count | Not stated on the pages reviewed | Not stated on the pages reviewed |
| Skill area 1 | Manage a security operations environment, 40 to 45% | Implement information protection, 30 to 35% |
| Skill area 2 | Respond to security incidents, 35 to 40% | Implement data loss prevention and retention, 30 to 35% |
| Skill area 3 | Perform threat hunting, 20 to 25% | Manage risks, alerts and activities, 30 to 35% |
| Query language | KQL, tested directly in the hunting domain | Not listed in the study guide |
| Other skills expected | Sentinel, Defender portal, automation | PowerShell, Entra, Defender portal, Defender for Cloud Apps |
| Exam price | Varies by country, typically USD 165 in the US (check the Microsoft page) | Same, typically USD 165 in the US (check the Microsoft page) |
| Validity | 12 months, free online renewal | 12 months, free online renewal |
| Skills outline effective | October 21, 2026 | October 28, 2026 |
| Retirement notice | None shown | None shown |
| Best for | SOC analysts, incident responders, threat hunters | Compliance, data protection, M365 and security admins |
| Typical next step | SC-500 or a hunting and detection specialisation | Governance, privacy or cloud security study |
The Short Answer
The two exams look like neighbours because both sit under “Security” in Microsoft’s catalogue, but they train for different days at work.
- SC-200 is about attackers. You watch alerts come in, decide what is real, trace what happened across endpoints, identities, email and cloud apps, contain it, and then go looking for threats nobody alerted on. Microsoft describes the candidate as someone who reduces organisational risk through triage, incident response, threat hunting and detection engineering.
- SC-401 is about data. You find sensitive information, label it, stop it leaving through the wrong channel, keep or delete it according to policy, spot risky insiders, and prove what happened when the legal team asks. Microsoft describes the candidate as someone who plans and implements information security for sensitive data using Microsoft Purview and related services, including data used by AI services.
If you picture yourself staring at an incident queue, SC-200 fits. If you picture yourself writing a DLP policy that stops a spreadsheet of customer records going to a personal email address, SC-401 fits.
Why This Comparison Matters Now
Both outlines were refreshed within the last two weeks, so older guides you find online may describe an earlier version.
- The SC-200 skills measured apply from October 21, 2026. The change log lists one minor update to the item about ingesting data into the Microsoft Sentinel SIEM and platform.
- The SC-401 skills measured apply from October 28, 2026. The change log lists one minor change to the sensitivity labels objective under information protection.
Neither page shows a retirement notice. That matters because several Microsoft credentials are retiring this year. If you want the wider picture, our guide to Microsoft certifications retiring in 2026 tracks which ones are affected. SC-200 and SC-401 are not on the notices shown in the pages reviewed for this article, but Microsoft can change that, so check the official page before booking.
Another reason for the timing: AI has moved into both exams. SC-401 now names data security posture management for AI in its risk domain, and SC-200 expects you to work with Sentinel’s newer data platform, including KQL jobs in the data lake. The two exams are both being pulled toward AI-era security, from different directions.
What SC-200 Covers
Microsoft lists three skill areas. Weights are given as ranges, so treat them as approximate.
| Skill area | Weight |
| Manage a security operations environment | 40 to 45% |
| Respond to security incidents | 35 to 40% |
| Perform threat hunting | 20 to 25% |
What this looks like in practice:
- Manage a security operations environment (40 to 45%): This is the largest domain, and it is about setting up and keeping the platform running. Expect Microsoft Defender XDR, Microsoft Sentinel, data ingestion into the Sentinel SIEM and platform, detections and analytics, and the way Microsoft Entra ID, Microsoft Purview and Defender for Cloud workload protections feed the picture.
- Respond to security incidents (35 to 40%): Triage and investigation of incidents across products, responding to threats, and automating responses so the same task does not need a human every time.
- Perform threat hunting (20 to 25%): Here KQL stops being background knowledge. The study guide names identifying the right table for a query, identifying threats with KQL, creating advanced hunting queries, and creating and managing KQL jobs in the data lake.
Microsoft’s own role description says the analyst performs hunting by using KQL and automates responses to threats. KQL is not listed as a formal prerequisite, but a fifth of the exam tests it directly, and it shows up inside the other two domains as well.
What SC-401 Covers
SC-401 splits almost evenly across three areas.
| Skill area | Weight |
| Implement information protection | 30 to 35% |
| Implement data loss prevention and retention | 30 to 35% |
| Manage risks, alerts and activities | 30 to 35% |
The study guide names these topics:
- Information protection: sensitive information types, document fingerprinting, exact data match, trainable classifiers, sensitivity labels, the Purview Information Protection client and scanner, and message encryption.
- Data loss prevention and retention: DLP policies, Adaptive Protection, Endpoint DLP, retention labels and policies, and recovering retained content.
- Risks, alerts and activities: Insider Risk Management, Purview Audit (Premium), eDiscovery, handling DLP and insider risk alerts, and data security posture management for AI.
Tools named across the guide include the Purview Data Explorer, Content Explorer and Activity Explorer, the Defender portal and Defender XDR, Defender for Cloud Apps, Microsoft Entra and PowerShell. Microsoft 365 workloads such as Exchange, SharePoint, Teams and Microsoft 365 Groups are the places where you apply the policies.
The study guide does not list KQL. If you have avoided query languages so far, SC-401 is the easier path into Microsoft security.
Where the Two Overlap
The overlap is smaller than the shared “SC” prefix suggests, but it is real.
- Defender portal and Defender XDR: both exams expect you to be at home in the portal. SC-200 uses it to investigate. SC-401 uses it to respond to alerts and to connect with Defender for Endpoint.
- Microsoft Purview: SC-401 is built on it. SC-200 touches it, since Purview signals help with incident investigation.
- Microsoft Entra: identity is background knowledge for both.
- Alerts: SC-200 handles security alerts. SC-401 handles DLP and insider risk alerts. The triage mindset transfers even though the products differ.
A practical way to see it: an SC-200 holder investigates how data was stolen, and an SC-401 holder designs the controls that should have stopped the data leaving. Strong teams need both, and that is why many people end up taking one after the other.
Difficulty: Which Is Harder?
For most people SC-200 is the harder exam, mainly because of KQL and the breadth of the products.
- KQL is a hard requirement in practice. About a fifth of the exam tests it directly, and you will struggle in the incident domain without it.
- More tooling. Defender XDR, Sentinel, Entra ID, Purview and Defender for Cloud all appear in the role description.
- Hands-on judgement. Triage questions ask you to choose the right next action, not recall a definition.
SC-401 is more about policy design and configuration. The pain points here are the sheer number of Purview features and how they differ. Many candidates confuse sensitivity labels with retention labels, DLP with Adaptive Protection, and Audit with eDiscovery. The exam rewards people who have actually built a policy and watched it fire.
If you already administer Microsoft 365, SC-401 will feel familiar. If you already work in a SOC, SC-200 will.
Who Should Take Which
Take SC-200 if:
- You work as, or want to become, a SOC analyst, incident responder or threat hunter.
- Your organisation runs Microsoft Defender XDR or Microsoft Sentinel.
- You are comfortable learning a query language and enjoy investigating.
- You want a Microsoft credential that maps to operations roles.
Take SC-401 if:
- You are a Microsoft 365 administrator, compliance officer or data protection specialist.
- Your organisation uses Microsoft Purview, or is rolling it out to prepare for AI tools such as Copilot.
- You work with privacy, retention or legal hold requests.
- You prefer policy design over investigation.
Take both, in this order, if:
- You work in a mid-sized security team where the same people cover operations and data protection. Start with whichever matches your current job, because the first exam should help you at work immediately. The second then widens your reach.
Six Realistic Scenarios
- Help desk technician who wants a first security job. SC-200 if the target is a SOC role. SC-401 if the target is an M365 admin or compliance job. Look at the job postings you want before choosing.
- M365 administrator told “we need to stop data leaks before we roll out Copilot”. SC-401. It maps directly to labels, DLP and DSPM for AI.
- SOC analyst at a company on Microsoft Sentinel. SC-200. You probably do most of it daily, and KQL practice at work counts toward the hunting domain.
- Compliance analyst moving from spreadsheets to Purview. SC-401. It gives structure to tools you are starting to use.
- Consultant selling Microsoft security services. Both, eventually. Clients buy operations and data protection projects in different budget cycles.
- Student with no work experience. Neither exam requires prior certification, but SC-200 expects security operations concepts and KQL. SC-401 is easier to reach with M365 and policy knowledge. Pick whichever job you can picture yourself doing.
Does One Pay Off More? Salary and Career Impact
I did not find a reliable survey that separates SC-200 holders from SC-401 holders, so I am not quoting a pay figure for either. Any number tied to a single Microsoft associate certificate would come from job-title averages, which also cover people who hold other credentials and different experience levels.
What can be said without inventing data:
- SC-200 maps to operations titles such as security analyst, SOC analyst, incident responder and threat hunter. Check job boards in your market for how often postings mention Sentinel or Defender.
- SC-401 maps to governance and data protection titles such as information security administrator, compliance analyst, technical privacy staff, and M365 security engineer. Organisations preparing for AI tools are asking more questions about data exposure, which is where this exam fits.
- Experience moves pay more than the certificate. The jump usually comes when you move up into senior or specialist roles, not when you pass the exam.
- A certificate helps most at transitions. It is a signal when you change role, employer or specialism.
To get a number for your own market, search for the job titles above, compare the ranges, and note how many postings mention Sentinel, Defender, Purview or the exam code. That will tell you more than any global average.
Cost and Renewal
- Exam fee: Microsoft’s pages say the price depends on the country or region where the exam is proctored. In the US, associate-level Microsoft exams have typically been USD 165, so confirm yours at checkout.
- Validity: both certifications expire after 12 months unless renewed.
- Renewal: free, done by passing an online assessment on Microsoft Learn.
- Retakes: after a failed attempt you can retake after a short waiting period. Check Microsoft’s current exam policies for the exact waiting time.
- Language: the English exam is updated first, and translations follow about eight weeks later. If your language is not available, Microsoft allows you to request an extra 30 minutes.
Budget separately for a lab. SC-200 practice is much better with access to a Sentinel workspace and sample data. SC-401 practice is better with a Microsoft 365 tenant where Purview features are available. A trial or a developer tenant, if you can get one, will save you from studying only from screenshots.
How to Prepare for SC-200
- Read the official study guide and mark every line as “do daily”, “have seen” or “never touched”.
- Learn KQL from the basics: where, project, summarize, join, extend, and time filters. Practise on real tables, not tutorials only.
- Set up Defender XDR and Sentinel in a trial or lab, connect a few data sources, and look at the incidents they create.
- Walk through an incident from alert to closure in the Defender portal, writing down which tool you used at each step.
- Practise writing hunting queries and turning one into a detection rule.
- Spend time on automation: what can be automated, and what must stay manual.
- Take timed practice tests and review every wrong answer. Our free SC-200 practice questions and the SC-200 exam page cover the format.
Plan on 6 to 10 weeks if you already work with security tools, and longer if KQL is new.
How to Prepare for SC-401
- Start from the study guide and the Purview portal. Click through every feature named in the guide, even if you never expect to use it.
- Build a sensitive information type, a sensitivity label with a policy, a DLP policy, and a retention label. Seeing each one apply to a file is the best revision.
- Learn the differences between similar features: sensitivity labels and retention labels, DLP and Adaptive Protection, Audit and eDiscovery.
- Configure Insider Risk Management policies and review the alerts they create.
- Revise the AI parts, especially data security posture management for AI.
- Brush up on PowerShell basics, since the guide lists it as an area of familiarity.
- Take timed practice tests and review each mistake. Our SC-401 exam page is a good starting point.
Plan on 4 to 8 weeks if you already administer Microsoft 365, and longer if Purview is new to you.
A Simple Decision Framework
Answer these four questions:
- Do I want to investigate and stop attacks, or design the controls that protect data? Investigate points to SC-200. Protect data points to SC-401.
- Am I willing to learn KQL? No means SC-401 first.
- What does my employer actually run? Sentinel or Defender XDR raises the value of SC-200. Purview and Copilot rollout raises the value of SC-401.
- Which job posting do I want to qualify for in the next 12 months? Pick the exam that appears most in those postings.
If you cannot decide, pick the exam whose product you already touch at work. A certificate you can practise on the job is cheaper to earn and easier to keep current.
Related Reading
If you are weighing a wider Microsoft security path, read SC-200 vs SC-300 and SC-300 vs SC-401 to see how these two compare with the identity exam. For the cloud security side, see AZ-500 vs SC-500. To see where each exam fits in the bigger picture, our top Microsoft certifications roadmap and cybersecurity career path guide are good places to continue.
FAQS
Which is better, SC-200 or SC-401?
Neither is better for everyone. SC-200 is better if you want a SOC, incident response or threat hunting role. SC-401 is better if you work on data protection, compliance or Microsoft 365 administration. Pick the one that matches the job you do or want.
Is SC-200 harder than SC-401?
For most people, yes. SC-200 tests KQL directly in its hunting domain (20 to 25%) and covers more products, including Defender XDR and Microsoft Sentinel. SC-401 is broad across Purview features but does not list KQL in its study guide.
Do I need KQL for SC-401?
No. The SC-401 study guide does not list KQL. It lists Microsoft Purview, the Defender portal, Defender for Cloud Apps, Microsoft Entra and PowerShell as the tools you should be familiar with.
Do I need KQL for SC-200?
Yes, in practice. Microsoft does not list it as a formal prerequisite, but the hunting domain tests it directly and the role description says the analyst performs hunting using KQL.
How long are the SC-200 and SC-401 exams?
Both are listed at 100 minutes. The pages reviewed do not state a fixed number of questions.
What is the passing score for SC-200 and SC-401?
700 or greater for both exams, on Microsoft’s scaled score.
How much do SC-200 and SC-401 cost?
Microsoft says the price depends on the country or region where the exam is proctored. In the US, associate-level Microsoft exams have typically been USD 165, but confirm the price for your location at checkout.
Do SC-200 and SC-401 expire?
Yes, both certifications are valid for 12 months. Renewal is free and done by passing an online assessment on Microsoft Learn.
Are SC-200 and SC-401 retiring?
The Microsoft pages reviewed for this article show no retirement notice for either exam. Both skills outlines were refreshed in October 2026, SC-200 on October 21 and SC-401 on October 28. Check the official page before booking, because Microsoft can change dates.
Can I take SC-401 without SC-200?
Yes. Neither exam is a prerequisite for the other, and Microsoft does not require an earlier certification for either one. You can take them in any order.
Which exam is better for a beginner in cybersecurity?
SC-401 is easier to reach if you already know Microsoft 365 and do not know a query language. SC-200 is the better target if you want a SOC job and are ready to learn KQL. Neither is a true entry-level exam, so some hands-on practice with the tools helps either way.
Is SC-401 worth it in 2026?
It is worth it if your organisation uses Microsoft Purview or plans to roll out AI tools that raise data exposure questions. The current outline includes data security posture management for AI, which links the exam to those projects. It is less useful if your employer does not use Microsoft 365.
Should I take both SC-200 and SC-401?
Take both if your work spans security operations and data protection, or if you consult on Microsoft security projects. Start with the exam that matches your current job, then add the second after you have used the first.
Final Thoughts
SC-200 is the right choice if you want to work the incident queue and hunt threats with KQL. SC-401 is the right choice if you want to design the labels, DLP and retention policies that keep data where it belongs. Both are current, both renew free every year, and both outlines were refreshed in October 2026. Read the latest study guide on Microsoft’s Security Operations Analyst Associate page before you book, since outlines and prices can change.