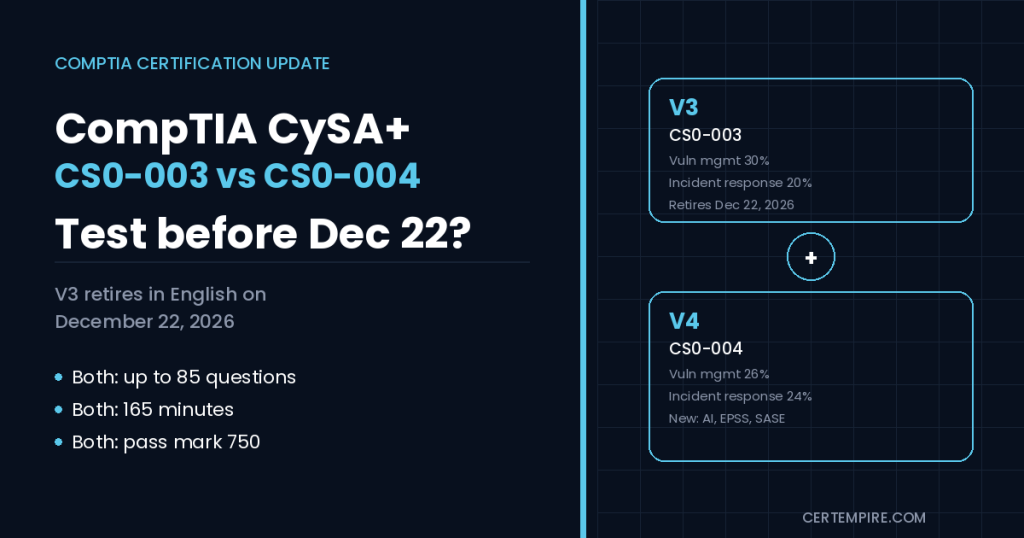
TL;DR: CompTIA’s CySA+ page says the English CS0-003 (V3) exam retires on December 22, 2026, and that CS0-004 (V4) is already available (launched June 23, 2026). Both versions allow up to 85 questions and pass at 750 on a 100 to 900 scale, so the format is nearly identical and the real differences are in content. V4 shifts weight toward incident response and security operations and away from vulnerability management, and it adds AI in security operations, EPSS-based vulnerability prioritization, Zero Trust and SASE topics, software supply chain risk (SBOM) and more reporting and metrics. The decision is simple. If you have not started studying yet, or you would need to cram to make the cutoff, go straight to CS0-004. If you are well into CS0-003 preparation and can realistically sit the exam before December 22, finishing V3 is a reasonable choice, and the credential you earn is the same CySA+ certification. Candidates who take the Japanese, Portuguese or Spanish exam have until March 23, 2027 on V3. Check the dates on CompTIA’s site before you book, because the retirement window is close.
Quick Facts
| Item | CySA+ V3 (CS0-003) | CySA+ V4 (CS0-004) |
| Status | Retiring | Current version, launched June 23, 2026 |
| English exam retirement | December 22, 2026 | None announced on the pages we reviewed |
| English learning products retire | November 22, 2026 | Not applicable |
| Translated exam retirement | March 23, 2027 (Japanese, Portuguese, Spanish) | Not applicable |
| Questions | Up to 85, multiple choice and performance-based | Up to 85, multiple choice and performance-based |
| Time | 165 minutes | 165 minutes |
| Passing score | 750 on a 100 to 900 scale | 750 on a 100 to 900 scale |
| Domains | Security Operations 33%, Vulnerability Management 30%, Incident Response and Management 20%, Reporting and Communication 17% | Security Operations 34%, Vulnerability Management 26%, Incident Response and Management 24%, Reporting and Communication 16% |
| Languages | English, Japanese, Portuguese, Spanish | English now. French, Japanese, Spanish and Portuguese listed as coming soon |
| Recommended experience | Network+, Security+ or equivalent knowledge, plus at least 4 years of hands-on work as an incident response analyst, SOC analyst or similar | About 4 years as a SOC analyst or vulnerability analyst (CompTIA’s pages give 3 to 4 years in one place and a minimum of 4 in another) |
| Voucher price (U.S. retail, per CompTIA’s V4 FAQ) | Not stated on the pages reviewed | USD 425 |
| Validity | 3 years | 3 years, renewable through CompTIA’s continuing education program |
Figures come from CompTIA’s CySA+ V3 and V4 pages and blog, checked in November 2026. CompTIA’s pages did not tell us whether CS0-003 vouchers can be used for CS0-004, so confirm that with CompTIA or your voucher provider before you buy or switch.
Key Takeaways
- Deadline: The English CS0-003 exam retires December 22, 2026. That is about six weeks from now, and the English learning products for V3 retire sooner, on November 22, 2026.
- Same credential, different content. Passing either version earns CySA+. The version only affects what you study.
- Format is the same. Up to 85 questions, 165 minutes and a 750 passing score on a 100 to 900 scale on both versions.
- Weights moved. Vulnerability Management drops from 30% to 26%. Incident Response and Management rises from 20% to 24%. Security Operations edges up from 33% to 34%. Reporting and Communication slips from 17% to 16%.
- New themes in V4: AI use cases, risks and governance in security work, EPSS-based prioritization, expanded Zero Trust and SASE coverage, AI-assisted SOC workflows, SBOM and software supply chain risk, identity-based attacks, cloud activity and reporting metrics.
- No new language options yet for V4. English is available now. Translated V4 exams are listed as coming soon.
- If you are starting from zero, V4 is the safer choice. Studying V3 material now means learning a version with a date on it.
- If you are nearly ready for V3, finishing it is reasonable, provided you can test with some buffer before December 22.
What Is CompTIA CySA+?
CySA+ is CompTIA’s intermediate cybersecurity analyst certification. It validates the skills of a SOC analyst or vulnerability analyst: monitoring and analyzing security data, managing vulnerabilities, responding to incidents and reporting findings clearly. It sits above Security+ and below the advanced SecurityX credential in CompTIA’s security stack. The V4 page says it is approved under DoD Directive 8140.03M, and CompTIA’s V4 FAQ says earning CySA+ also renews eligible lower-level certifications, including Security+.
For where CySA+ fits among other CompTIA options, see our CompTIA certification roadmap. If you are comparing it with SecurityX, our CySA+ vs SecurityX guide covers that decision, and our guide to becoming a cybersecurity analyst shows how CySA+ fits into a career path.
What Is the Difference Between CS0-003 and CS0-004?
The format is almost identical, but the content is updated for AI, modern architecture and risk-based vulnerability work. The biggest changes are the added AI coverage, the heavier weight on incident response and the expanded vulnerability prioritization methods.
Domain weights, side by side
| Domain | V3 (CS0-003) | V4 (CS0-004) | Change |
| Security Operations | 33% | 34% | +1 |
| Vulnerability Management | 30% | 26% | -4 |
| Incident Response and Management | 20% | 24% | +4 |
| Reporting and Communication | 17% | 16% | -1 |
What the shift tells you:
- Incident response matters more. A four-point rise means roughly three or four more questions on a full-length exam if the weights are applied to the 85-question maximum.
- Vulnerability management still matters, but the emphasis on pure scanning and scoring gives way to prioritization methods.
- Security operations remains the largest domain, at a third of the exam on both versions.
- Reporting and communication stays at about one-sixth. Do not skip it, since it often rewards careful reading.
Topic changes, V3 to V4
CompTIA’s V4 FAQ and press release highlight these shifts:
| Area | V3 (CS0-003) | V4 (CS0-004) |
| AI | Limited coverage | AI use cases, risks and governance, including uses such as log analysis and automation and risks such as hallucinations and data exposure |
| Vulnerability prioritization | Traditional approaches | Expanded EPSS-based prioritization, plus risk-based approaches |
| Architecture | Basic Zero Trust | Expanded Zero Trust Network Access (ZTNA) and SASE |
| Security operations | SIEM and SOAR focus | AI-assisted SOC workflows and more automation |
| Software security | Standard software assurance topics | Stronger SBOM and software supply chain risk coverage |
| Threat detection | Established detection methods | More attention to identity-based attacks, cloud activity and social engineering |
| Reporting | Reporting and communication | Linking technical findings to business impact through reporting and KPIs |
CompTIA describes V4 as focused on real-world tasks in SOC environments, with applied, scenario-based skills across the security operations lifecycle, from threat hunting and vulnerability management to incident response and stakeholder communication.
What Does Each CySA+ Domain Test?
The topics below combine CompTIA’s published highlights with the kinds of tasks analysts typically practice. They are a study guide, not an official scope list. Download the official CS0-004 objectives from CompTIA and use them as your checklist.
Security Operations (34% on V4)
This domain is about monitoring, detecting and analyzing activity.
- Log and data analysis. Reading logs, correlating events and spotting anomalies.
- Tools and platforms. SIEM, SOAR and endpoint tools, and how analysts use them to triage alerts.
- Threat intelligence and hunting. Using indicators and behavior patterns to find suspicious activity.
- Identity and cloud activity. V4 gives more attention to identity-based attacks and cloud events.
- AI in operations. Where AI helps, such as log analysis and automation, and where it introduces risk.
- Scripting and automation awareness. Recognizing what simple automation does and where it speeds up SOC work.
Vulnerability Management (26% on V4)
This domain is about finding weaknesses and deciding what to fix first.
- Scanning and assessment. Interpreting scanner output and separating true from false positives.
- Prioritization. Using severity, exploitability and business context. V4 expands EPSS-based approaches.
- Remediation planning. Patching, compensating controls and tracking fixes.
- Software supply chain. SBOM concepts and third-party risk.
- Attack surface and architecture. How Zero Trust, ZTNA and SASE change exposure.
Incident Response and Management (24% on V4)
This domain is about handling security events from detection to recovery.
- The incident lifecycle. Preparation, detection, containment, eradication, recovery and lessons learned.
- Evidence and forensics basics. Preserving data and following procedures.
- Playbooks and escalation. Knowing what to do first and who to inform.
- Attack analysis. Mapping behavior to attack techniques and stages.
- Post-incident work. Documentation and improvements.
Reporting and Communication (16% on V4)
This domain is about turning technical findings into decisions.
- Reports and metrics. KPIs, trends and dashboards that matter to stakeholders.
- Communication. Writing for technical and nonspecialist audiences.
- Vulnerability and incident reporting. What to include and how to prioritize it.
- Process improvement. Using findings to change policy or controls.
Should You Take CS0-003 or CS0-004?
Take CS0-004 if you have not started or if you need more than a few weeks to prepare. Take CS0-003 only if you are close to ready and can sit the exam before December 22 with a buffer. Today is about six weeks from the English retirement date, so time is the deciding factor.
Decision scenarios
| Your situation | Better choice | Why |
| Not started studying | CS0-004 | Learn the current version and avoid a deadline |
| Studying CS0-003 for a few weeks, not close to ready | CS0-004 | Most core skills transfer, and you avoid cramming |
| Nearly ready for CS0-003 with two to three weeks of study left | CS0-003, if you can sit well before December 22 | You keep your momentum, but leave a buffer for retakes |
| Already booked CS0-003 for a December date | CS0-003, but confirm your date is before December 22 and consider a backup plan | Late scheduling risk |
| Would fail CS0-003 and want to retake | CS0-004 | A retake after December 22 would need V4 anyway for English |
| Taking the exam in Japanese, Portuguese or Spanish | CS0-003 is still available until March 23, 2027, but V4 translations are listed as coming soon | Check availability in your language |
| Need the newest AI and Zero Trust content for your job | CS0-004 | These topics are emphasized in V4 |
| Employer or contract asks for a specific exam code | Follow the requirement | Confirm with the employer |
A simple timeline test
Count the weeks between today and December 22, 2026.
- Subtract at least two weeks as a buffer for a possible retake or scheduling issues.
- Subtract the weeks of study you still need.
- If the result is positive, V3 is realistic. If it is zero or negative, switch to V4.
How Much of CS0-003 Study Carries Over to CS0-004?
Most of it. Both versions cover the same four areas, and the core analyst skills (log analysis, vulnerability scanning, incident response, reporting) are shared. If you have already studied V3, you do not start over for V4. You add the new topics.
| Topic | Carries over? |
| Log analysis, SIEM and SOAR basics | Yes, with extra focus on automation and AI |
| Vulnerability scanning and scoring | Yes, plus EPSS and risk-based prioritization |
| Incident response lifecycle | Yes, with a heavier weight on V4 |
| Threat intelligence and hunting | Yes |
| Reporting and communication | Yes, with more attention to metrics and business impact |
| AI in security operations | New focus, so study it separately |
| ZTNA and SASE | Expanded in V4 |
| SBOM and software supply chain | Expanded in V4 |
| Identity-based attacks and cloud activity | More attention in V4 |
A practical way to switch: finish your core V3 review, then spend two to three weeks on the V4 gap topics and V4 practice questions.
How Hard Is CySA+ Compared With Security+?
CySA+ is generally treated as a step up from Security+ because it is analysis-heavy and scenario-based. CompTIA recommends about four years of hands-on experience as a SOC or vulnerability analyst, whereas Security+ targets a baseline. That experience level is a recommendation, not a requirement, and many candidates sit CySA+ with less, but they should plan on a longer study period. CompTIA does not publish pass rates on the pages we reviewed, so treat any figure you see online as unofficial.
Where candidates often struggle:
- Performance-based questions. They require applied analysis, such as reading logs or choosing a response, and take longer than multiple-choice items.
- Scenario wording. Several answers can be technically valid, and you must pick the best next step.
- Tools without hands-on practice. Reading about a SIEM is not the same as using one.
How Long Should You Study?
CompTIA’s V4 FAQ gives two study-time ranges (30 to 55 hours and 30 to 40 hours) without explaining the difference. Treat those as a rough starting point, and plan more time if you do not already work in a SOC. The weekly plans below are our planning estimates, not CompTIA guidance.
A 6-week CS0-004 plan
| Week | Focus | Hands-on task |
| 1 | Read the objectives. Security operations: logs, SIEM, SOAR and threat intelligence | Read sample logs and write down what each event means |
| 2 | Identity, cloud and endpoint detection, plus AI in security operations | List three ways AI helps an analyst and three risks |
| 3 | Vulnerability management: scanning, scoring and EPSS-based prioritization | Take a sample scan result and rank findings by risk |
| 4 | Zero Trust, ZTNA, SASE, SBOM and software supply chain | Draw a Zero Trust access flow for a small company |
| 5 | Incident response lifecycle, playbooks, forensics basics and post-incident work | Write a one-page playbook for a phishing incident |
| 6 | Reporting and metrics, then timed practice sets and performance-based questions | Two full timed sets, then review every miss |
A 3-week V3 sprint (only if you are already close)
| Week | Focus |
| 1 | Review weak domains from your practice scores |
| 2 | Timed full-length practice and performance-based questions |
| 3 | Final review, then sit the exam with at least a two-week buffer before December 22 |
For practice material on V3, see our CySA+ CS0-003 guide, our CS0-003 exam questions and our free CySA+ practice test. To understand the architecture topics that grew in V4, read our Zero Trust security guide.
How Do You Handle Exam Day?
Plan for about two minutes per question on average, since you have up to 165 minutes for up to 85 questions, but performance-based questions take longer.
- Decide your performance-based question plan in advance. Many candidates flag them and return after the multiple-choice items. That is a common approach, not a CompTIA rule.
- Read the last sentence first. Find out what is being asked, then read the scenario for clues.
- Look for the best next step. CySA+ questions often ask what to do first or what is most appropriate.
- Do not skip the objectives. Reporting and communication questions are easy to lose if you treat them as common sense.
- Leave review time. Revisit flagged items with a clear head.
What Mistakes Should You Avoid?
The most common mistakes are leaving the V3 decision too late, studying the wrong version and neglecting performance-based practice.
- Waiting past the retirement window. A December 22 deadline leaves little room for a retake if your first attempt does not go well.
- Mixing study material. Check the exam code on every course, book and practice test.
- Assuming a voucher transfers. CompTIA’s pages did not say whether V3 vouchers work for V4, so confirm before you switch.
- Ignoring the new V4 topics. AI, EPSS, ZTNA, SASE and SBOM are highlighted in V4 material, so do not skip them if you take V4.
- Skipping hands-on practice. Use sample logs, scan results and incident scenarios.
- Underestimating reporting and communication. It is 16 to 17% of the exam.
- Ignoring language availability. If you need a non-English exam, check which versions are currently offered.
What Should You Take After CySA+?
SecurityX is CompTIA’s advanced security certification, and many analysts also add cloud or vendor-specific security credentials. CySA+ also renews eligible lower-level certifications, including Security+, according to CompTIA. To see how Security+ is changing too, read our SY0-701 vs SY0-801 guide, and for the wider security-and-AI picture see our AI security certifications guide.
FAQS
When does the CySA+ CS0-003 exam retire?
CompTIA’s CySA+ page says the English CS0-003 exam retires on December 22, 2026. English learning products retire on November 22, 2026. Japanese, Portuguese and Spanish versions retire on March 23, 2027.
What is the difference between CS0-003 and CS0-004?
The format is nearly the same, but CS0-004 adds more on AI in security operations, EPSS-based prioritization, Zero Trust and SASE, SBOM and software supply chain risk, and reporting metrics. It also shifts weight toward incident response.
Should I take CS0-003 or CS0-004?
Take CS0-004 if you have not started or need more than a few weeks to prepare. Take CS0-003 only if you are nearly ready and can sit the exam before December 22 with a buffer for a possible retake.
Is CS0-004 harder than CS0-003?
CompTIA does not publish pass rates on the pages we reviewed, so there is no official answer. The format and passing score are the same, but V4 adds topics such as AI use and risks, which may be new if you have not worked with them.
How many questions are on CySA+ CS0-004, and how long is the exam?
Up to 85 questions in 165 minutes, with multiple-choice and performance-based questions. The passing score is 750 on a scale of 100 to 900.
What are the CS0-004 domains and weights?
Security Operations 34%, Vulnerability Management 26%, Incident Response and Management 24% and Reporting and Communication 16%.
What were the CS0-003 domains and weights?
Security Operations 33%, Vulnerability Management 30%, Incident Response and Management 20% and Reporting and Communication 17%.
Can I use a CS0-003 voucher for CS0-004?
CompTIA’s pages we reviewed did not say. Confirm with CompTIA or your voucher provider before you buy or switch.
How much does the CySA+ CS0-004 exam cost?
CompTIA’s V4 FAQ lists a U.S. retail voucher price of USD 425, and mentions bundles, training packages and promotions. Prices vary, so confirm in CompTIA’s store.
How much experience do I need for CySA+?
CompTIA recommends about four years of hands-on experience as a SOC analyst or vulnerability analyst. It is a recommendation, not a requirement. Its pages also mention three to four years in one place, so treat it as a range.
How long is CySA+ valid, and how do I renew it?
Three years. You renew through CompTIA’s continuing education program, either with a single activity such as passing the latest version of the exam or with a combination of activities. Check CompTIA’s site for current unit counts.
Is CS0-004 available in languages other than English?
CompTIA’s V4 page lists English now, with French, Japanese, Spanish and Portuguese coming soon. Check CompTIA’s site for current availability before you book.
Does passing CySA+ renew Security+?
According to CompTIA’s V4 FAQ, earning CySA+ also renews eligible lower-level certifications, including Security+. Confirm the current rules in your CompTIA account.
Final Thoughts
The retirement date makes this a time-boxed decision. If you are early in your preparation, move to CS0-004 now and spend your time on the current content, including the AI, vulnerability prioritization and Zero Trust topics that V4 emphasizes. If you are close to ready for CS0-003, book your exam soon, leave a buffer before December 22 and have a clear plan to switch to V4 if something slips. Whichever version you choose, match every voucher and study resource to the exam code, use CompTIA’s objectives as your checklist and confirm current dates, prices and language options on CompTIA’s official CySA+ V4 page before you register.