
DRAG DROP You have several model-driven apps. You must ensure that app creators and system administrators can customize the apps. You must follow the principle of least privilege. You need to assign the permissions that are needed for app creators and system administrators. Which security roles should you assign? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point 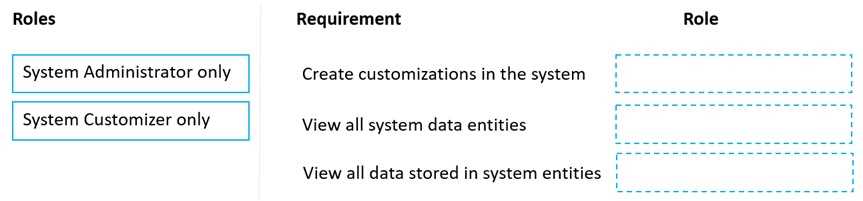
System Customizer lets you create customizations and see the metadata/entities but not all the stored data. System Administrator is needed for full data visibility. Mapping should be: create customizations and view entities = System Customizer only, view all stored data = System Administrator only. Pretty sure that fits least privilege best, agree?
System Customizer is enough for creating customizations and viewing the entity list or schema, since that's their main purpose-they just can't access every record in all tables. System Administrator is needed when you actually have to view all data stored, which requires higher privileges. So it's Create customizations & View data entities = System Customizer only, View all stored data = System Administrator only. Pretty sure that's right but let me know if I missed something obvious.
Yeah, System Customizer for creating customizations and viewing entities, but only System Administrator should see all the actual stored data. So mapping is: create customizations and view entities -> System Customizer only, view all stored data -> System Administrator only. That sticks to least privilege. Anyone see it differently?