Free Fortinet NSE7_SOC_AR-7.6 Practice Test Questions and Answers (2026)

Last Update Check
View Mode
Q: 1
Which of the following are critical when analyzing and managing events and incidents in a SOC? (Choose two answers)
Options
Q: 2
Review the incident report. Shortly after being compromised, an infected host collected its own network configuration and connection details, then began sending low-volume connection attempts to multiple internal addresses to identify responding hosts. Which two MITRE ATT&CK techniques best describe this activity? Choose two answers.
Options
Q: 3

You are using FortiSIEM analytics to reference the configuration management database (CMDB) event type categories with the following requirements: Attribute: Event Type Value: Group: Logon Success Which operator must you use for the analytics search? Choose one Answer

Options
Q: 4
Which three are threat hunting activities? (Choose three answers)
Options
Q: 5
Based on the Pyramid of Pain model, which two statements accurately describe the value of an indicator and how difficult it is for an adversary to change? (Choose two answers)
Options
Q: 6

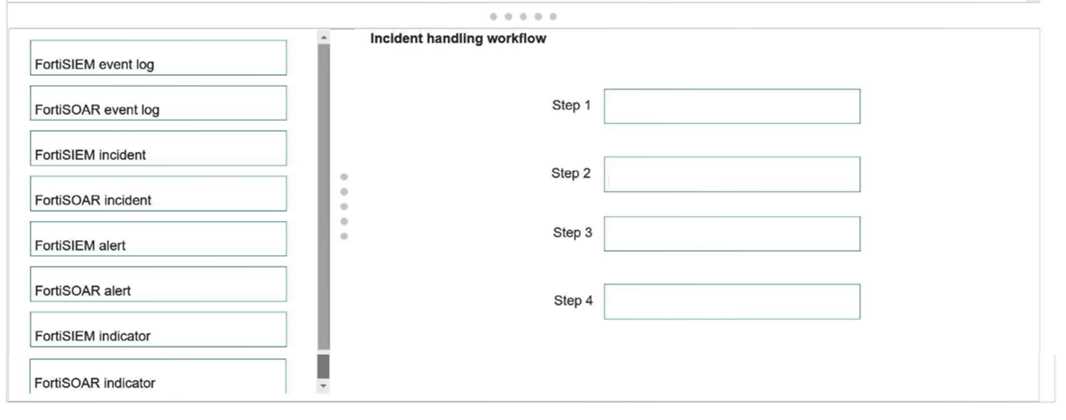
Using the default data ingestion wizard in FortiSOAR, place the incident handling workflow from FortiSIEM to FortiSOAR in the correct sequence. Select each workflow component in the left column, hold and drag it to a blank position in the column on the right. Place the four correct workflow components in order, placing the first step in the first position at the top of the column. Fortinet NSE7 SOC AR 7 question

Drag & Drop
Q: 7

Refer to the exhibit.

PDF Exam dumpWhat is the correct Jinja expression to filter the results to show only the MD5 hash values?

{{ [slot 1]|[slot 2][slot 3].[slot 4] ") }}


Select the Jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first step in the first slot. Once you place an expression, you can move it again if you want to change your answer before moving to the next question. You need to drop four Jinja expressions in the work area.


Select and drag the screen divider to change the viewable area of the source and work areas.PDF Exam dump

Drag & Drop
Q: 8

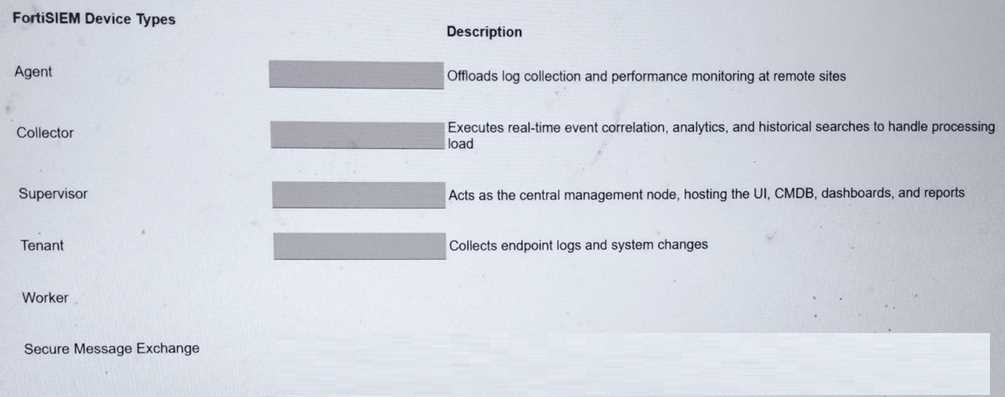
Match the FortiSIEM device type to its description. Select each FortiSIEM device type in the left column, hold and drag it to the blank space next to its corresponding description in the column on the right. Fortinet NSE7 SOC AR 7 question

Drag & Drop
Q: 9

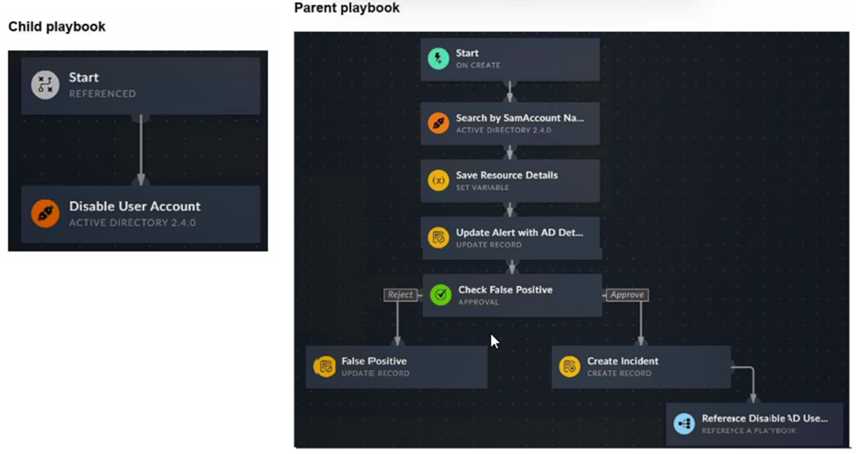
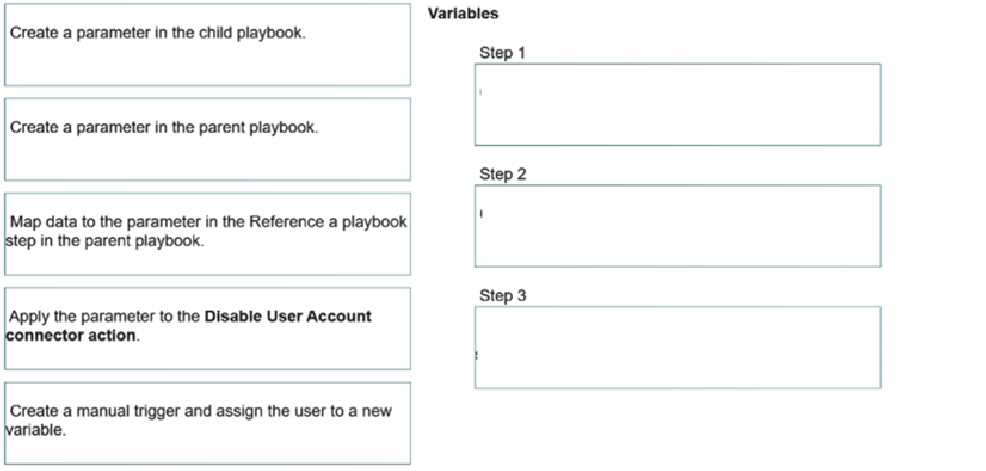
Refer to the exhibits. Fortinet NSE7 SOC AR 7 question You have a playbook that, depending on whether an analyst deems the alert to be a true positive, could reference a child playbook. You need to pass variables from the parent playbook to the child playbook. Place the steps needed to accomplish this in the correct order. Fortinet NSE7 SOC AR 7 question
Drag & Drop
Q: 10
Which two phases are part of the FortiSOAR incident handling process but are not phases in the NIST 800-61 Revision 2 model? Choose two answers.
Options
Question 1 of 20

Premium Access Includes

  • Quiz Simulator
  • Exam Mode
  • Progress Tracking
  • Question Saving
  • Flash Cards
  • Drag & Drops
  • 3 Months Access
  • PDF Downloads
Get Premium Access
Scroll to Top