Free FCP_FMG_AD-7.6 Practice Test Questions and Answers (2026)

Last Update Check

View Mode
Q: 1
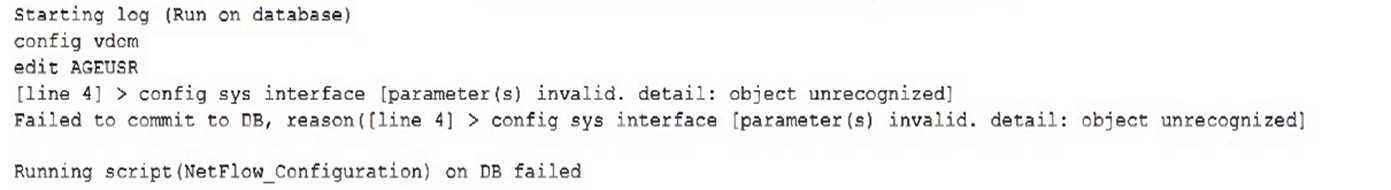
While attempting to push a NetFlow configuration script through the FortiManager policy package: an administrator encounters an error stating that an object is unrecognized in line 4. FCP FMG AD 7 question What must the administrator do to successfully apply the NetFlow configuration script and avoid the object unrecognized error?
Options
34 comments in the community discussion
6
C. not D this time. The error comes from using a VDOM name as an IP address variable and only custom metadata with the actual IP will work for source-ip. If we were talking interface names, D might fit, but that's not what this script is doing. Makes sense?
2
C . The key is that $(vdom) just gives you the VDOM name, not a real IP, so using custom metadata variables to assign the correct source IP per VDOM fixes it. Not 100% if there's a sneaky scenario but that's how it usually works.
Q: 2
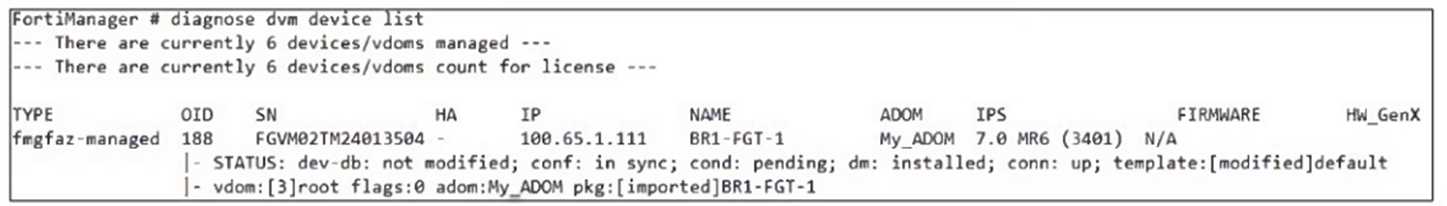
Refer to the exhibit. FCP FMG AD 7 question Which two statements about the output are true? (Choose two.)
Options
20 comments in the community discussion
1
If they're asking about current status, then A and D fit. The "Modified" highlights the DB mismatch (A), and the template override logic (D) is default FMG behavior. But if they'd specified after install, C could flip in. Anyone else catch that fine print?
1
Had something like this in a mock. Pretty sure it's A and D. "Modified" shows the config isn't matching the device DB (A), and applying a provisioning template will override device-level configs (D). That's usually what they're testing with that status output. If anyone disagrees, let me know.
Q: 3
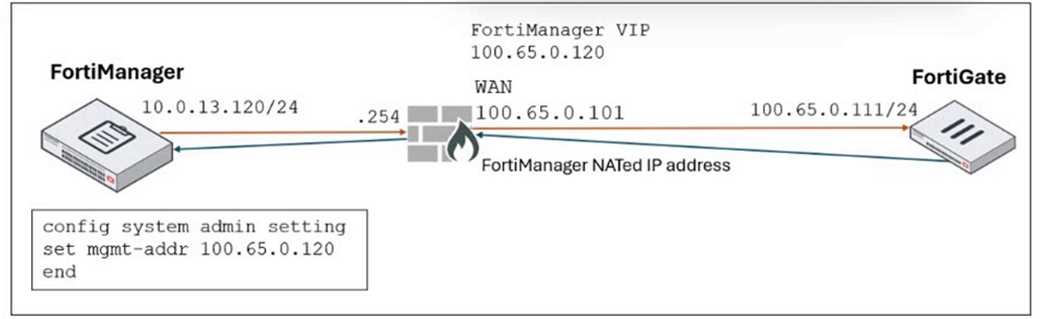
Refer to the exhibit. FCP FMG AD 7 question FortiManager is operating behind a network address translation (NAT) device, and the administrator configured the FortiManager NATed IP address under the FortiManager system administration settings. What is the expected result during discovery?
Options
27 comments in the community discussion
1
Always with the NAT questions... D is what matches similar practice exams. When a NATed IP is set in FortiManager, FortiGate learns that public 100.65.0.120 for central management-not both, not internal. Pretty sure that's right, correct me if you see it working differently.
1
C . Sometimes FortiManager just pushes the internal IP (100.65.0.101), especially if something about the NAT config isn't synced right. Not totally sure, but that's what I've seen in labs.
Q: 4
An administrator must create a policy and install it on a FortiGate device within an ADOM in backup mode. How can the administrator perform this task?
Options
25 comments in the community discussion
6
Option D is correct, based on what I've read in practice questions. In backup mode you lose central management so can't use the policy package or install wizard. Scripts are basically the only supported method to push changes directly to FortiGate. Fortinet docs and official admin guide both mention this limitation. Le
1
Yeah, it's D here.
Q: 5
You want to let multiple administrators work in the same ADOM without creating configuration conflicts. What is the best and the most effective solution to apply?
Options
25 comments in the community discussion
3
D. seen similar in practice sets. Workspace mode is what actually locks the ADOM so you won't get config overlaps, way more direct than workflow mode for this use case. Pretty sure D fits what they're after here, but I'd double-check if the question was about approvals instead.
1
Workspace mode (D) makes sense here since it's specifically built to prevent admins from overwriting each other in the same ADOM. I've seen this called out in Fortinet's official docs and in a few practice exams. Not 100% sure if workflow (B) could also count, but workspace is usually what's expected for conflict pr
Q: 6
A service provider administrator has assigned a global policy package to a managed customer ADOM named My_ADOM. The customer administrator has access only to My_ADOM. How can the customer administrator edit the global header policy of the global policy package?
Options
30 comments in the community discussion
1
D , these global header bits are always locked unless you're the service provider admin. Seen similar on other practice sets, and it's frustrating how little flexibility customer admins have. Would love to hear if anyone's actually managed to edit from My_ADOM though.
1
D
Q: 7
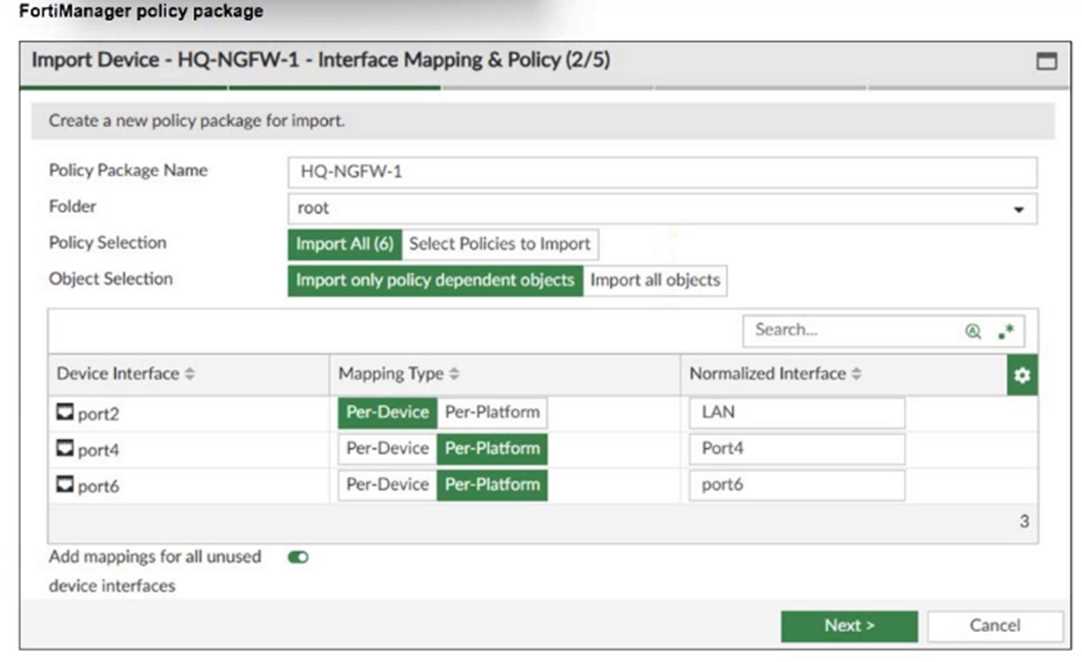
Refer to the exhibit. FCP FMG AD 7 question An administrator added a FortiGate device to FortiManager with the default object settings at the ADOM layer. What can you conclude from the import policy package process of the HQ-NGFW- 1 device?
Options
24 comments in the community discussion
6
C . If the wizard actually shows 'Create New' for LAN, port4, and port6, then FortiManager is going to add those as normalized interfaces in the ADOM. That's standard behavior in the import process. Pretty sure that's what they're asking here, but open to corrections.
5
Option C The trap is thinking manual steps are needed (like B), but FortiManager creates those missing interfaces during import if mapping is set to "Create New". Seen this on practice exams, pretty sure it's C.
Q: 8
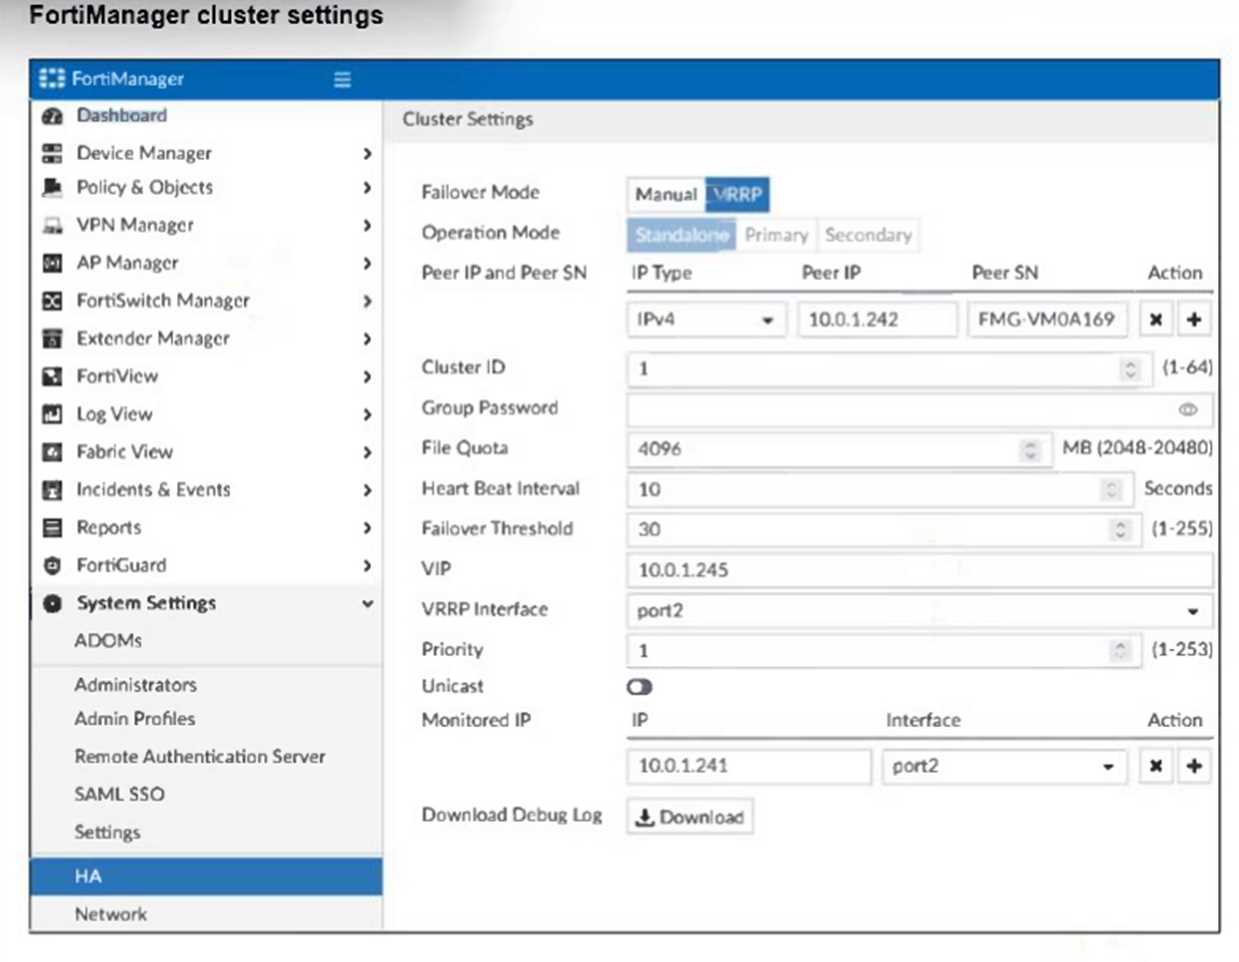
Refer to the exhibit. FCP FMG AD 7 question If the monitored interface for the primary FortiManager device fails, what must you do to maintain high availability (HA)?
Options
21 comments in the community discussion
6
Option A. saw this type in a practice exam before and HA failover is just automatic if config is good.
2
A, I remember a similar question from labs and it's always automatic unless HA config is broken.
Q: 9
After correcting a policy package configuration issue, you want to prevent administrators from repeating the mistake that caused the issue. Which FortiManager approach best meets this need?
Options
23 comments in the community discussion
5
Makes sense to pick D here. Workflow approval actually blocks the same misconfig from being applied again. Pretty confident on this one.
2
Option D but does "best" here mean totally prevents or just reduces risk? If repeat mistakes aren't critical, C might work too.
Q: 10
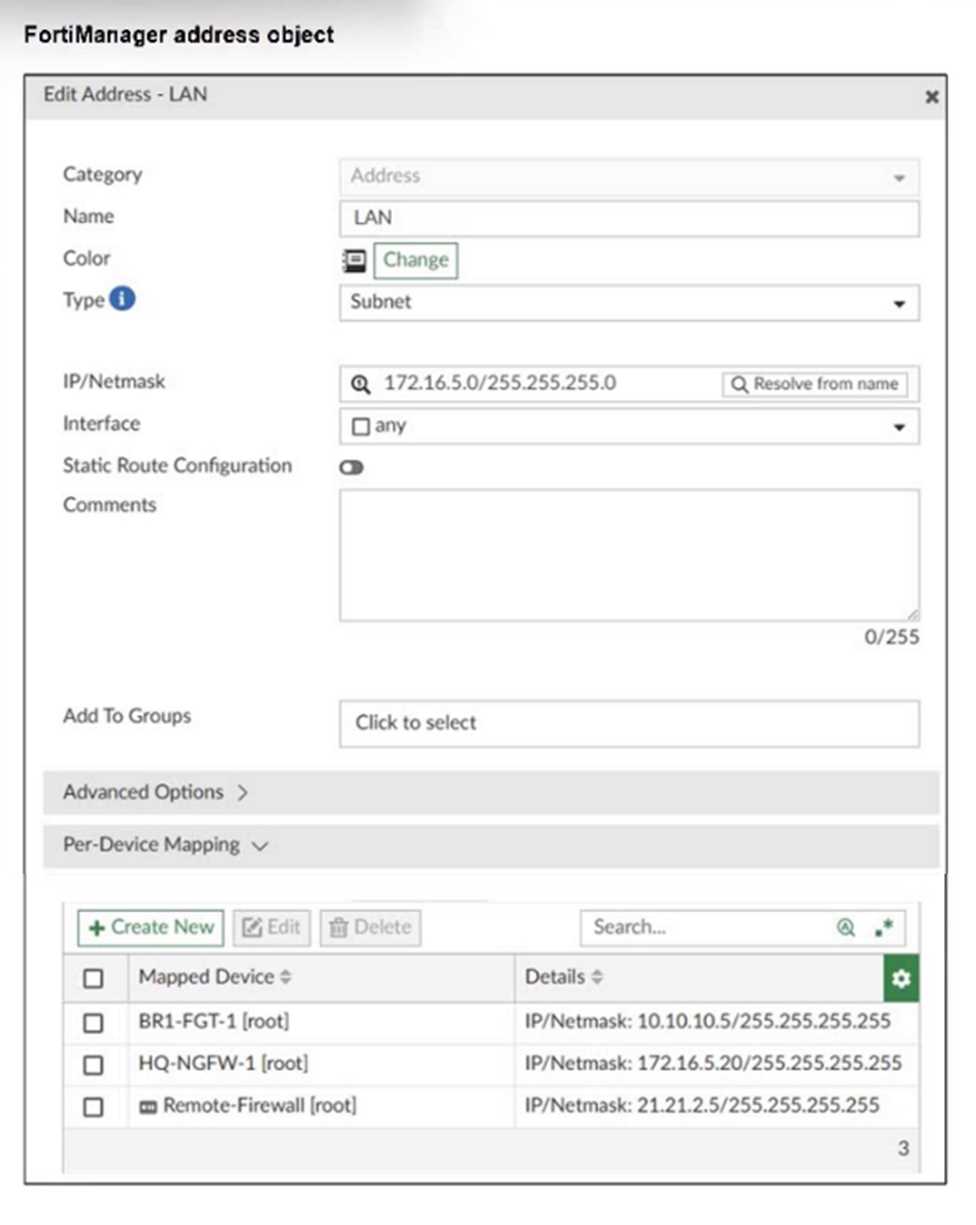
Refer to the exhibit. FCP FMG AD 7 question An administrator has created a firewall address object that is used in multiple policy packages for multiple FortiGate devices in an ADOM. After the installation operation is performed, which IP/netmask will be installed on Remote-Firewall [VDOM1] for the LAN firewall address object?
Options
23 comments in the community discussion
2
A . C is tempting for the subnet but per-device mapping overrides default every time.
2
Option A is correct for this. With per-device mapping enabled, FortiManager pushes the mapped value (21.21.2.5/255.255.255.255) to Remote-Firewall [VDOM1], not the default address object value. Pretty sure that's how object overrides work, but open if someone sees it differently.
Question 1 of 20

Premium Access Includes

  • Quiz Simulator
  • Exam Mode
  • Progress Tracking
  • Question Saving
  • Flash Cards
  • Drag & Drops
  • 3 Months Access
  • PDF Downloads
Get Premium Access
Scroll to Top