Q: 1
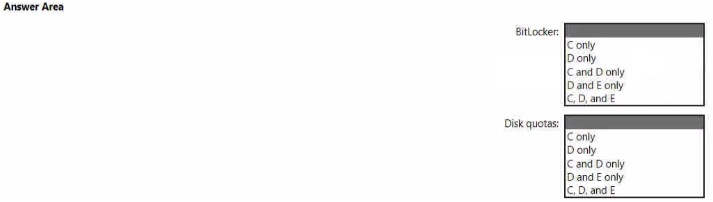
You have a server named Server1 that runs Windows Server and contains three volumes named C, D, and E.
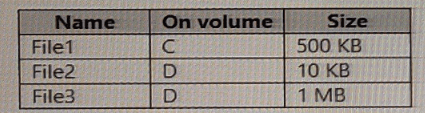
Files are stored on Server1 as shown in the following exhibit: File1 (volume C, 500 KB), File2 (volume D, 10
KB), File3 (volume D, 1 MB). For volume D, Data Deduplication is enabled and set to General purpose file
server. You perform the following actions: move File1 to volume D; copy File2 to volume D and name the
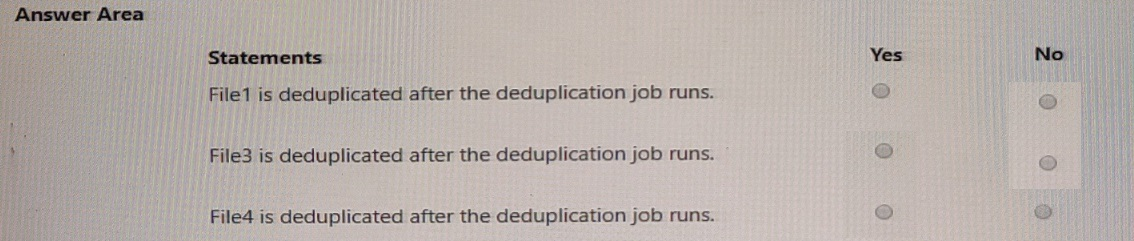
copy File4; move File3 to volume E. For each of the following statements, select Yes if the statement is true.
Otherwise, select No. NOTE: Each correct selection is worth one point.
 QUESTION IMAGE:
QUESTION IMAGE:
Your Answer
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
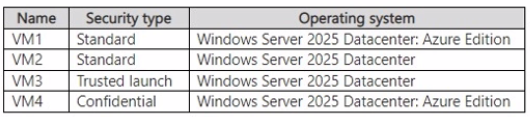 Virtual machines with their security type and operating system
 App1 Properties - General tab
 App1 Properties - Failover tab
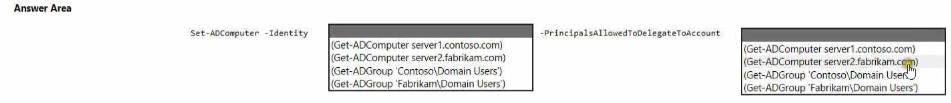
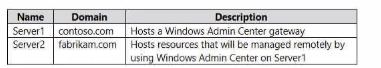 You need to configure resources based constrained delegation so that the users In contoso.com can use
Windows Admin Center on Server) to connect to Server? How should you complete the command? To
answer, select the appropriate options in the answer are
a. NOTE: Each correct selection is worth one point.
QUESTION IMAGE:
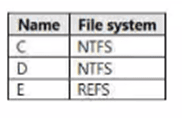 Volumes on Server1
QUESTION IMAGE:
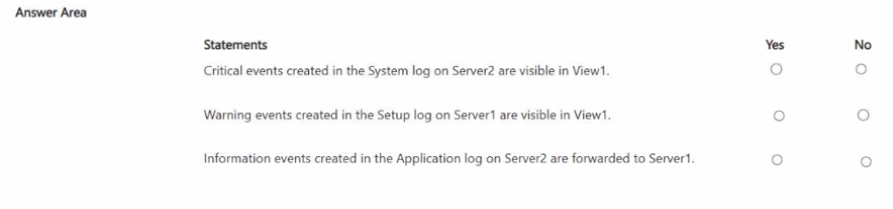
 Subscription1 Query Filter settings
QUESTION IMAGE:
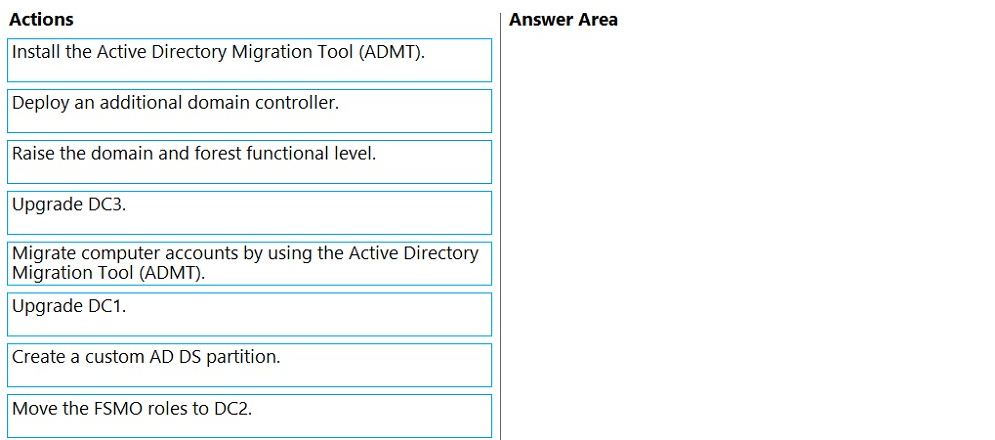
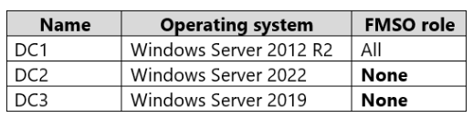 You need to raise the forest functional level to Windows Server 2016. The solution must meet the following
requirements:
* Ensure that there are three domain controllers after you raises the level.
* Minimize how long the FSMO roles are unavailable.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list
of actions to the answer area and arrange them in the correct order.
Exhibit
QUESTION IMAGE: