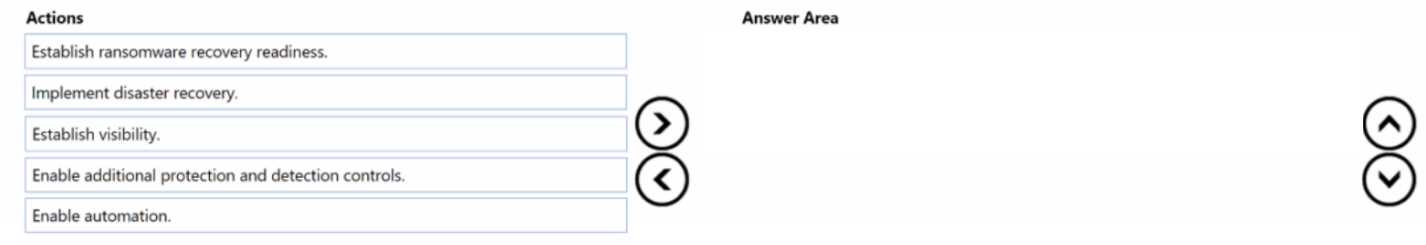
NIST Special Publication 800-207: Zero Trust Architecture, Section 3.2.1, Core Components and Zero Trust Principles. (Emphasizes visibility and monitoring as a fundamental requirement for the policy engine to function—a prerequisite for effective controls and automation.)
Microsoft Zero Trust Deployment Guide, Pillars and Capabilities. (Details the progression: Identity, Endpoints, Data, Apps, Infrastructure, Network, and the required controls. Visibility and comprehensive protection/detection are recurring themes.)
MITRE ATT&CK Framework, Tactics and Techniques: Detection and Response. (Highlights that effective SOC response and automation require high-fidelity detection and protection controls as inputs. Automation is the key to efficient scaling of security operations.)
SANS Institute, Security Operations Center (SOC) Best Practices. (Consistently identifies automation as the most significant contributor to increasing SOC efficiency and reducing analyst burnout, but requires prior visibility and detection capabilities.)
IEEE Security & Privacy Magazine, "Zero Trust Security: A Survey of Architectures and Practices," 2023. (Discusses the need for ubiquitous monitoring (visibility) before enforcing granular policies (controls) and the role of Security Orchestration, Automation, and Response (SOAR) in operationalizing Zero Trust.)