
Q: 9
DRAG DROP [Security Concepts] Drag and drop the features of Cisco ASA with Firepower from the left onto the benefits on the right. 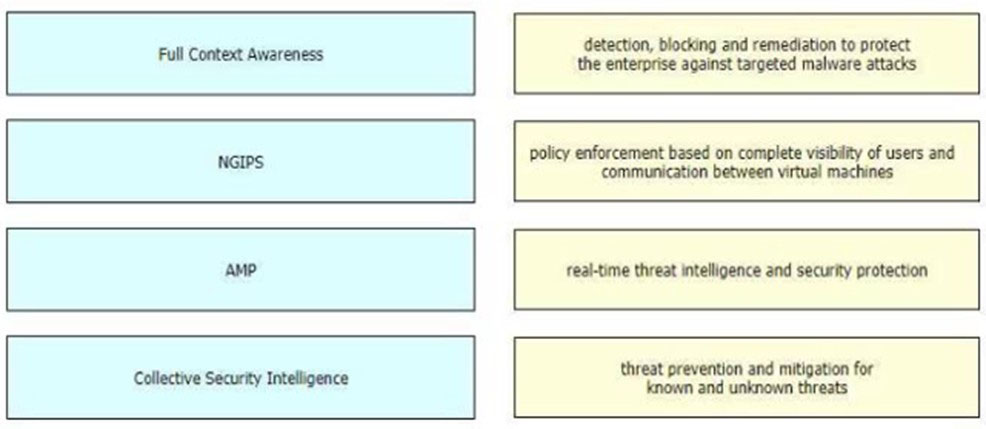
Drag & Drop
Discussion
Don’t think NGIPS should be on the detection/blocking/remediation line. AMP is Cisco’s advanced malware solution, so more aligned with that benefit. The proper mapping is: AMP → detection/blocking/remediation, Full Context Awareness → policy enforcement with visibility, Collective Security Intelligence → real-time threat intel, NGIPS → threat prevention/mitigation. Others might put NGIPS first, but exam wording points to this order.
AMP → detection, blocking and remediation; Full Context Awareness → policy enforcement with user/VM visibility; Collective Security Intelligence → real-time threat intelligence; NGIPS → threat prevention and mitigation for known/unknown threats. Got this mapping from Cisco docs too. Only slight uncertainty is if AMP and NGIPS ever swap, but pretty sure this is right since AMP is for malware and NGIPS handles broader threat types. Anyone see it different?
C . The main thing with patching is cutting down risks from known threats, not just getting new features or disabling protocols. That regular patch cycle really keeps vulnerabilities in check. Pretty sure that's what Cisco's looking for here, but open if anybody thinks otherwise.
AMP to detection, blocking and remediation; Full Context Awareness to policy enforcement with user/VM visibility; Collective Security Intelligence to real-time threat intelligence; NGIPS to threat prevention and mitigation. Seen similar exam mappings-easy to mix up NGIPS and AMP but NGIPS is broader. Pretty sure this is right, but open to corrections if anyone thinks otherwise.
Full Context Awareness → detection, blocking and remediation; NGIPS → policy enforcement with visibility; AMP → threat prevention and mitigation for known/unknown threats; Collective Security Intelligence → real-time threat intel. I matched NGIPS to visibility since it inspects flows, and AMP for the broader mitigation part. Might be off on one, but that's how I remembered from lab work. What do you guys think?
Nah, the right mapping should be AMP to detection/blocking/remediation, Full Context Awareness to policy enforcement with visibility, Collective Security Intelligence to real-time threat updates, and NGIPS to threat prevention/mitigation. Easy to mix up NGIPS and AMP here since both do detection but NGIPS is broader. Disagree?
Definitely sticking with C here.
Its C, saw similar in exam reports. Key point is cutting down known vulnerabilities.
A sounds possible to me. Getting new features from patches can be pretty important for endpoints since it boosts capabilities and sometimes even makes support easier. Not totally sure though, maybe that's more of a bonus than the main reason?
If the question said "best reason for patching" instead of just "important," would that change whether C is correct or not?
Be respectful. No spam.