Free Fortinet NSE6_EDR_AD-7.0 Practice Test Questions and Answers (2026)

Last Update Check
View Mode
Q: 1
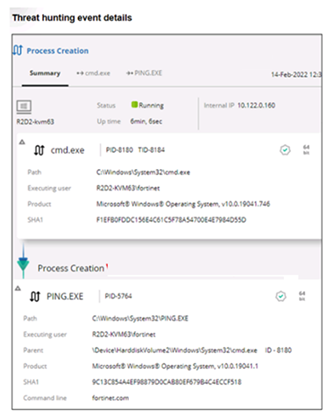
Refer to the exhibit. Fortinet NSE6 EDR AD 7 question Based on the threat hunting event details shown in the exhibit, which two statements about the event are true? (Choose two answers)
Options
Q: 2
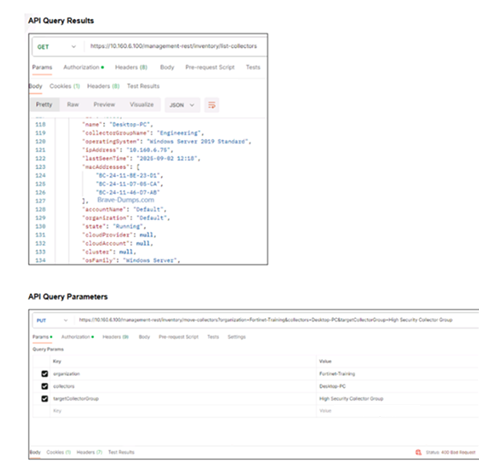
Refer to the exhibits. Fortinet NSE6 EDR AD 7 question You are attempting to move a collector into the High Security Collector Group for isolation but encounter an error in the API request as shown in the exhibit. To successfully isolate the collector, which API parameter must you correct? (Choose one answer)
Options
Q: 3
Which two statements correctly describe the IoT probing process on FortiEDR? (Choose two answers)
Options
Q: 4
You are deploying FortiXDR alongside your FortiEDR 7.0 infrastructure to provide extended detection and response across multiple Fortinet products. During the integration setup, you need to configure how FortiEDR will correlate security events with data from your FortiGate firewall and FortiProxy. Which integration method does FortiXDR use to collect and correlate events from these products?
Options
Q: 5
You are asked to configure a query to run every 15 minutes, automatically searching for specific registry modifications across all endpoints. Which FortiEDR feature must you configure? (Choose one answer)
Options
Q: 6
Refer to the exhibits. Fortinet NSE6 EDR AD 7 question The application policy logs and application details are shown. Collector C8092231196 is a member of the Finance group. In this scenario, what must you do to block the FileZilla application? (Choose one answer)
Options
Q: 7
A playbook is configured with two actions: terminate process and isolate device. The terminate process action fails because the process is protected by Windows. What is the expected behavior for the second action, isolate device? (Choose one answer)
Options
Q: 8
While investigating a suspected data exfiltration incident, you use FortiEDR's threat hunting capabilities to search for endpoints that accessed sensitive files in your data repository. You have configured a scheduled query to run daily and send alerts when the threshold of file access events exceeds 50 per hour. The next morning, you receive an alert but notice the query has returned results for endpoints that legitimately access these files as part of normal backup operations. What should you do to refine your threat hunting profile?
Options
Q: 9
You discovered that a newly installed collector does not display on the Inventory tab in the central manager. Which two troubleshooting steps must you perform? (Choose two answers)
Options
Q: 10
What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)
Options
Question 1 of 20

Premium Access Includes

  • Quiz Simulator
  • Exam Mode
  • Progress Tracking
  • Question Saving
  • Flash Cards
  • Drag & Drops
  • 3 Months Access
  • PDF Downloads
Get Premium Access
Scroll to Top