Free 312-49v10 Practice Test Questions and Answers (2026)
Last Update Check
Q: 1
What is the default IIS log location?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 2
Charles has accidentally deleted an important file while working on his Mac computer. He wants to
recover the deleted file as it contains some of his crucial business secrets. Which of the following tool
will help Charles?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 3
Which file is a sequence of bytes organized into blocks understandable by the system’s linker?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 4
In both pharming and phishing attacks an attacker can create websites that look similar to legitimate
sites with the intent of collecting personal identifiable information from its victims. What is the
difference between pharming and phishing attacks?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 5
Jacky encrypts her documents using a password. It is known that she uses her daughter’s year of
birth as part of the password. Which password cracking technique would be optimal to crack her
password?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 6
Shane has started the static analysis of a malware and is using the tool ResourcesExtract to find more
details of the malicious program. What part of the analysis is he performing?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 7
Jason discovered a file named $RIYG6VR.doc in the C:\$Recycle.Bin\\ while analyzing a
hard disk image for the deleted dat
a. What inferences can he make from the file name?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 8
A forensic examiner is examining a Windows system seized from a crime scene. During the
examination of a suspect file, he discovered that the file is password protected. He tried guessing the
password using the suspect’s available information but without any success. Which of the following
tool can help the investigator to solve this issue?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 9
Which of the following attacks allows an attacker to access restricted directories, including
application source code, configuration and critical system files, and to execute commands outside of
the web server’s root directory?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 10
Report writing is a crucial stage in the outcome of an investigation. Which information should not be
included in the report section?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 11
Centralized binary logging is a process in which many websites write binary and unformatted log
data to a single log file. What extension should the investigator look to find its log file?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 12
When performing a forensics analysis, what device is used to prevent the system from recording data
on an evidence disk?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 13
Where should the investigator look for the Edge browser’s browsing records, including history, cache,
and cookies?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 14
What is the capacity of Recycle bin in a system running on Windows Vista?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 15
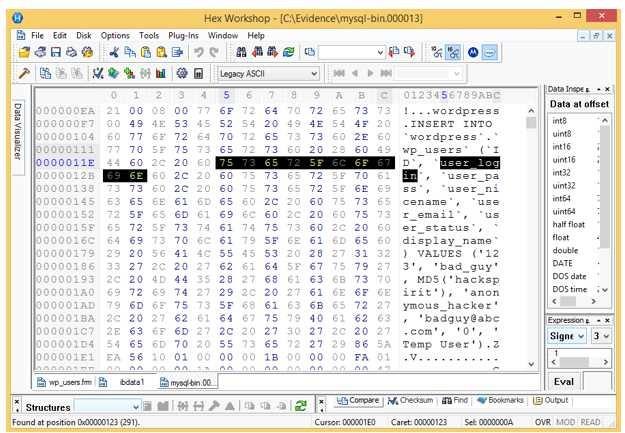
Analyze the hex representation of mysql-bin.000013 file in the screenshot below. Which of the
following will be an inference from this analysis?


Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 16
Select the tool appropriate for finding the dynamically linked lists of an application or malware.
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 17
To check for POP3 traffic using Ethereal, what port should an investigator search by?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 18
John is working on his company policies and guidelines. The section he is currently working on covers
company documents; how they should be handled, stored, and eventually destroyed. John is
concerned about the process whereby outdated documents are destroyed. What type of shredder
should John write in the guidelines to be used when destroying documents?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Q: 19
If you discover a criminal act while investigating a corporate policy abuse, it becomes a publicsector
investigation and should be referred to law enforcement?
Options
Discussion
No comments yet. Be the first to comment.
Be respectful. No spam.
Question 1 of 20