
DRAG DROP You have a Microsoft Sentinel workspace named workspace1 and an Azure virtual machine named VM1. You receive an alert for suspicious use of PowerShell on VM1. You need to investigate the incident, identify which event triggered the alert, and identify whether the following actions occurred on VM1 after the alert: The modification of local group memberships The purging of event logs Which three actions should you perform in sequence in the Azure portal? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. 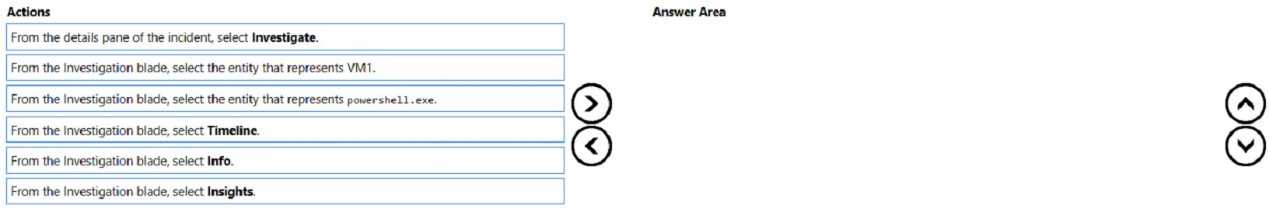
Insights → VM1 entity → Investigate is the order that lines up with Sentinel workflow for post-alert action checks. Insights gives you the overall context, then drilling into the VM1 entity lets you focus on actions at the machine level, and finally Investigate opens up full incident detail. I think this is what the question wants since it asks about group changes and log purges (not just process). Anyone disagree?
I don't think picking the PowerShell.exe entity is right here. Sentinel wants you to go via Insights first, then focus on the VM1 entity, then Investigate. The trap is jumping to process-level before checking machine context. Seen similar workflow called out in practice sets - Insights → VM1 entity → Investigate.