
HOTSPOT You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR. You discover a malicious process that was initiated by a file named File1exe on a device named Device1. You need to create a KQL query that will identify when File1.exe was created. The solution must meet the following requirements: • Return the FileName, InitiatingProcessFileName, and InitiatingProcessCommandLine columns. • Minimize the volume of data returned. How should you complete the query? To answer, select the appropriate options in the answer area. 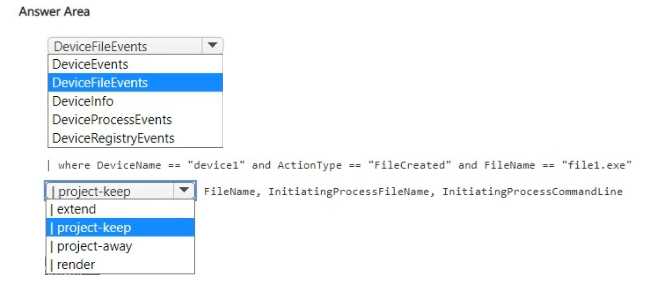
Actually, for finding when a file was created, you want FileCreationEvents instead of ProcessEvents. It gives you exactly the info needed and reduces unnecessary data. Pretty sure that's what Microsoft recommends for this scenario, unless I'm missing something?