
Q: 14
DRAG DROP An organization plans to deploy Azure storage services. You need to configure shared access signature (SAS) for granting access to Azure Storage. Which SAS types should you use? To answer, drag the appropriate SAS types to the correct requirements. Each SAS type may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content. NOTE: Each correct selection is worth one point. 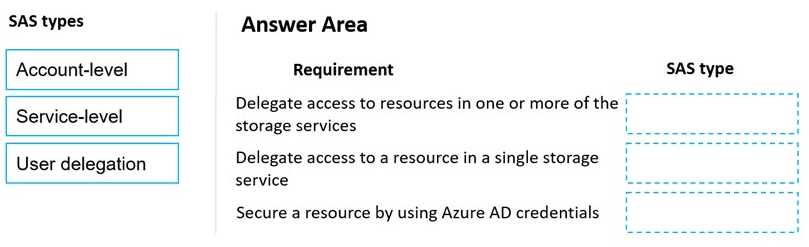
Drag & Drop
Discussion
Account-level → Delegate to one or more services, Service-level → just a single storage service, User delegation → Secure with Azure AD creds. That’s how I’d map it. I think that's right but maybe there’s overlap for the first two in rare cases?
Account-level -> Delegate access to resources in one or more of the storage services
Service-level -> Delegate access to a resource in a single storage service
User delegation -> Secure a resource by using Azure AD credentials.
Nice, the requirements are really clear here. Pretty sure this matches what I've seen on practice sets.
Service-level -> Delegate access to a resource in a single storage service
User delegation -> Secure a resource by using Azure AD credentials.
Nice, the requirements are really clear here. Pretty sure this matches what I've seen on practice sets.
Account-level → Delegate access to resources in one or more storage services, Service-level → Delegate access to a resource in a single storage service, User delegation → Secure a resource using Azure AD creds. That's how I see the mapping. Account-level gives you broad scope, service-level is more granular, and user delegation is the only one with AAD integration. Pretty sure that's right but not 100% if account/service ever overlap for cross-resource tasks. Someone disagree?
Be respectful. No spam.