
Q: 19
DRAG DROP [Security Concepts] Drag and drop the Firepower Next Generation Intrusion Prevention System detectors from the left onto the correct definitions on the right. 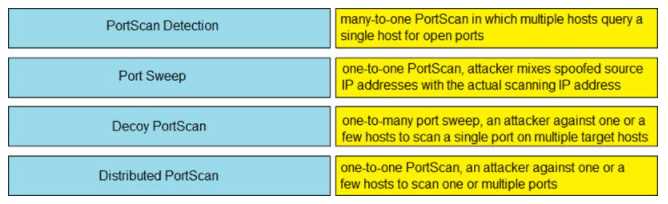
Drag & Drop
Discussion
Seen similar on practice, I'd map it as: Distributed PortScan → many-to-one, Decoy PortScan → one-to-one with spoofing, Port Sweep → one-to-many single port, PortScan Detection → one-to-one multiple ports. Not 100% sure if Decoy and Distributed trip people up sometimes, though.
Nah, I think Distributed PortScan should be matched with many-to-one. Trap is mixing up port sweep and decoy.
A bit unsure since the stem says "many-to-one" for Distributed PortScan, but what if the question was actually asking for the first response detected instead of the scan type? That would shift my mapping. Official guides or Firepower docs might clarify how they define these terms.
- PortScan Detection → one-to-one PortScan, attacker against one or a few hosts to scan one or multiple ports
- Port Sweep → many-to-one PortScan in which multiple hosts query a single host for open ports
- Decoy PortScan → one-to-many port sweep, an attacker against one or a few hosts to scan a single port on multiple target hosts
- Distributed PortScan → one-to-one PortScan, attacker mixes spoofed source IP addresses with the actual scanning IP address
Be respectful. No spam.