FortiSIEM applies tags to FortiClient EMS-managed hosts through FortiEMS integration. The
FortiSIEM 7.4 User Guide states that FortiSIEM supports discovery of FortiEMS servers using the
FortiEMS Management Server API with username/password authentication. That supports option A:
FortiEMS API credentials must be configured on FortiSIEM. The same guide explains that after
FortiEMS discovery, “FortiSIEM can tag or untag a host, using classification tags on FortiEMS server.”
It further explains the ZTNA workflow: in ZTNA, these tags are imported by Fortinet devices,
especially FortiGate firewalls, and referenced in ZTNA firewall rules. That supports option C: the tag
value used for ZTNA classification must be available/defined for the FortiEMS tagging workflow.
Option B is not the best required configuration in the question because a remediation script is an
execution method, not one of the two foundational settings being asked for. Option D reverses the
API relationship; FortiSIEM connects to FortiEMS using FortiEMS credentials, not FortiSIEM API
credentials stored on EMS.
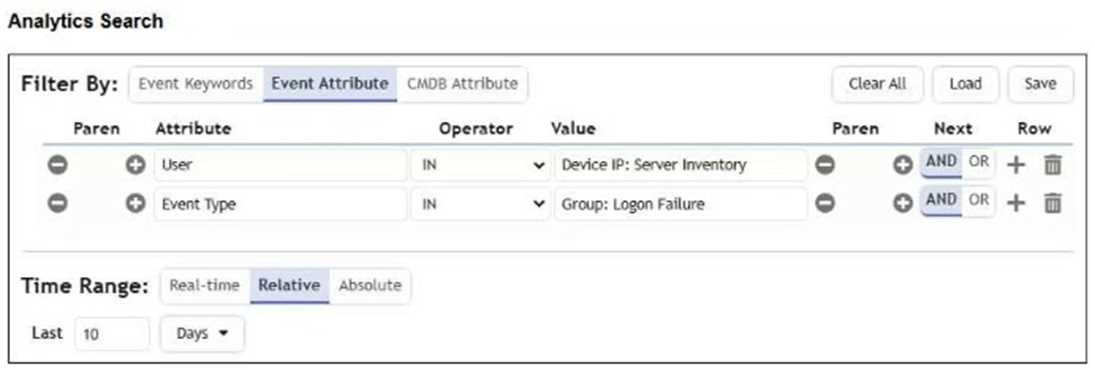 The analyst is troubleshooting the analytics query shown in the exhibit. Why is this search not producing any results?
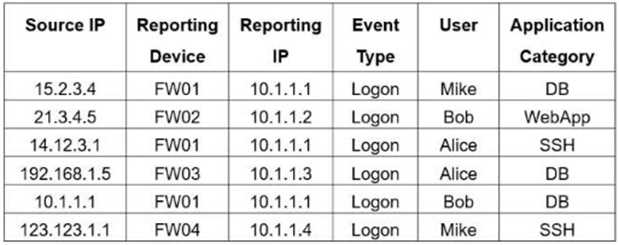 If you group the events by Reporting Device, Reporting IP, and Application Category, how many results will FortiSIEM display?
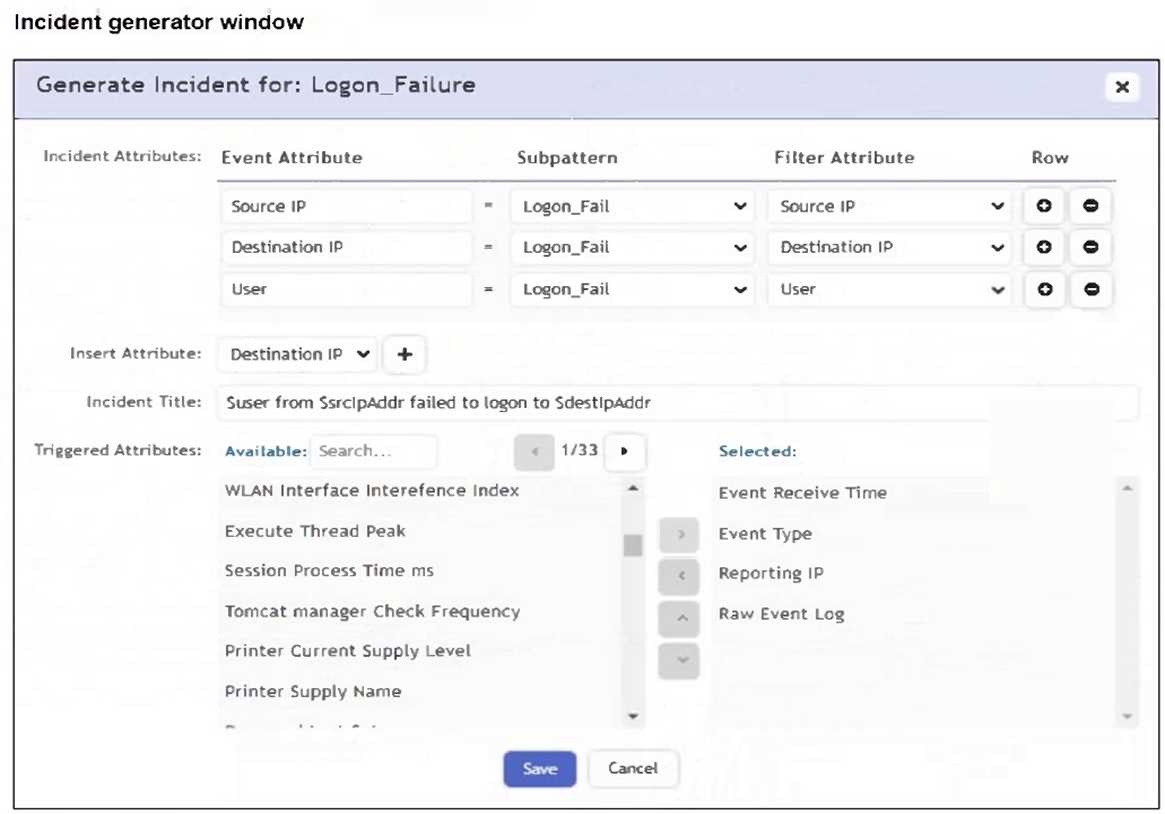 An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add Destination Host Name as an incident attribute. What must be changed to allow the analyst to select Destination Host Name as an attribute?
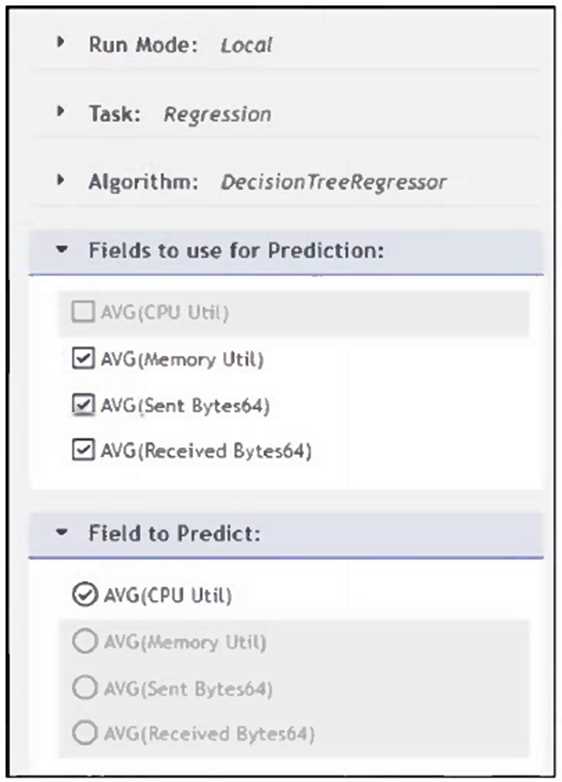 What will happen when a device being analyzed by the machine learning configuration shown in the exhibit has consistently high memory utilization?
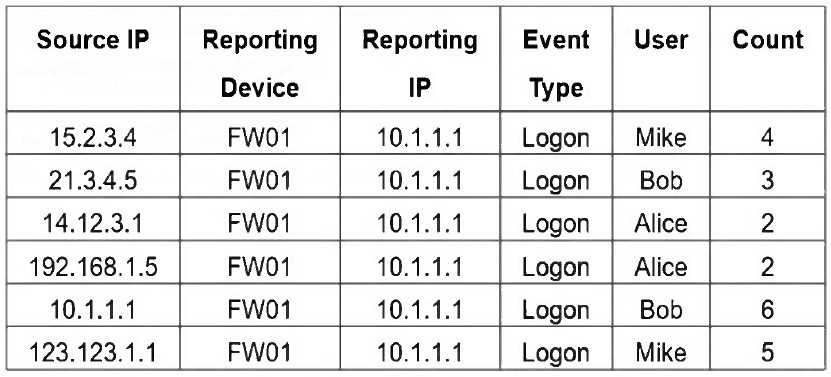 If you group the events by User and Count attributes, how many results will FortiSIEM display?