Free CFR-410 Practice Test Questions and Answers (2026)

Last Update Check

View Mode
Q: 1
A security operations center (SOC) analyst observed an unusually high number of login failures on a particular database server. The analyst wants to gather supporting evidence before escalating the observation to management. Which of the following expressions will provide login failure data for 11/24/2015?
Options
Q: 2
An administrator investigating intermittent network communication problems has identified an excessive amount of traffic from an external-facing host to an unknown location on the Internet. Which of the following BEST describes what is occurring?
Options
Q: 3
While performing routing maintenance on a Windows Server, a technician notices several unapproved Windows Updates and that remote access software has been installed. The technician suspects that a malicious actor has gained access to the system. Which of the following steps in the attack process does this activity indicate?
Options
Q: 4
What are three examples of incident response? (Choose three.)
Options
Q: 5
Which of the following types of attackers would be MOST likely to use multiple zero-day exploits executed against high-value, well-defended targets for the purposes of espionage and sabotage?
Options
Q: 6
When attempting to determine which system or user is generating excessive web traffic, analysis of which of the following would provide the BEST results?
Options
Q: 7
A system administrator has been tasked with developing highly detailed instructions for patching managed assets using the corporate patch management solution. These instructions are an example of which of the following?
Options
Q: 8
A suspicious script was found on a sensitive research system. Subsequent analysis determined that proprietary data would have been deleted from both the local server and backup media immediately following a specific administrator’s removal from an employee list that is refreshed each evening. Which of the following BEST describes this scenario?
Options
Q: 9
Which common source of vulnerability should be addressed to BEST mitigate against URL redirection attacks?
Options
Q: 10
Which three answer options are password attack methods and techniques? (Choose three.)
Options
Q: 11
A security analyst has discovered that an application has failed to run. Which of the following is the tool MOST likely used by the analyst for the initial discovery?
Options
Q: 12
Which of the following attacks involves sending a large amount of spoofed User Datagram Protocol (UDP) traffic to a router’s broadcast address within a network?
Options
Q: 13
A company help desk is flooded with calls regarding systems experiencing slow performance and certain Internet sites taking a long time to load or not loading at all. The security operations center (SOC) analysts who receive these calls take the following actions: - Running antivirus scans on the affected user machines - Checking department membership of affected users - Checking the host-based intrusion prevention system (HIPS) console for affected user machine alerts - Checking network monitoring tools for anomalous activities Which of the following phases of the incident response process match the actions taken?
Options
Q: 14

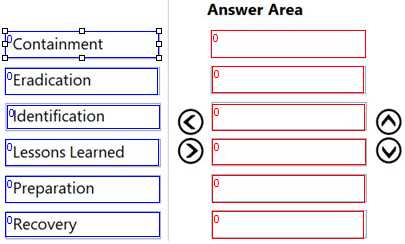
DRAG DROP What is the correct order of the DFIR phases? CertNexus CFR 410 question

Drag & Drop
Q: 15
Which of the following should normally be blocked through a firewall?
Options
Q: 16
After imaging a disk as part of an investigation, a forensics analyst wants to hash the image using a tool that supports piecewise hashing. Which of the following tools should the analyst use?
Options
Q: 17
Which of the following backup strategies will result in the shortest backup time during weekdays and use the least amount of storage space but incur the longest restore time?
Options
Q: 18
A common formula used to calculate risk is: + Threats + Vulnerabilities = Risk. Which of the following represents the missing factor in this formula?
Options
Q: 19
An automatic vulnerability scan has been performed. Which is the next step of the vulnerability assessment process?
Options
Q: 20
An attacker intercepts a hash and compares it to pre-computed hashes to crack a password. Which of the following methods has been used?
Options
Question 1 of 20

Premium Access Includes

  • Quiz Simulator
  • Exam Mode
  • Progress Tracking
  • Question Saving
  • Flash Cards
  • Drag & Drops
  • 3 Months Access
  • PDF Downloads
Get Premium Access
Scroll to Top