Free 312-49v10 Practice Test Questions and Answers (2026)

Last Update Check

View Mode
Q: 1
What is the default IIS log location?
Options
27 comments in the community discussion
5
Option B, A is a trap since it skips the logs folder. Pretty sure exam wants B as default.
1
It's B, default has both "logs" and "LogFiles". A is a common trap people fall for.
Q: 2
Charles has accidentally deleted an important file while working on his Mac computer. He wants to recover the deleted file as it contains some of his crucial business secrets. Which of the following tool will help Charles?
Options
36 comments in the community discussion
5
Option C not D. DriveSpy’s a Windows tool but FileSalvage is actually built for Mac, so makes sense here.
3
Option C FileSalvage for sure. Only one here built for Mac file recovery. Pretty sure that's what the question wants.
Q: 3
Which file is a sequence of bytes organized into blocks understandable by the system’s linker?
Options
34 comments in the community discussion
5
Yeah, not A. The linker processes object files, not executables. Option C is correct here since object files contain the necessary blocks and symbol info. Executable (A) is a common trap because it sounds like the final product. Pretty sure C is right but let me know if there's another view.
2
Its C, since object files (.obj or .o) are what the linker actually reads and merges. Source files go to the compiler first, not straight to the linker. Seen this in practice labs too, but open to correction if I missed something.
Q: 4
In both pharming and phishing attacks an attacker can create websites that look similar to legitimate sites with the intent of collecting personal identifiable information from its victims. What is the difference between pharming and phishing attacks?
Options
22 comments in the community discussion
1
Pharming changes the way your computer resolves domain names, so even if you type the correct URL, you get redirected to a fake site. Phishing usually involves tricking you into clicking on a link that looks legit but actually isn't. Option B explains this distinction clearly. I think that's what EC Council expects her
1
B is right here. Pharming uses DNS or hosts file changes to redirect legit URLs, phishing tricks users with links that look real but are actually fake sites. Pretty sure that's the core difference, unless the question changed focus to just social engineering. Let me know if you see it differently.
Q: 5
Jacky encrypts her documents using a password. It is known that she uses her daughter’s year of birth as part of the password. Which password cracking technique would be optimal to crack her password?
Options
40 comments in the community discussion
4
A . Rule-based lets you add specific patterns like a 4-digit year to your wordlist, way more efficient than brute forcing everything or just mixing words and numbers at random. Not 100% but fits best for the info given.
2
Option A since a rule for common years targets this exact edge case, not seeing another that fits better.
Q: 6
Shane has started the static analysis of a malware and is using the tool ResourcesExtract to find more details of the malicious program. What part of the analysis is he performing?
Options
41 comments in the community discussion
6
Option B makes sense. ResourcesExtract pulls embedded resources and string tables from executables, which lines up with a static strings search. Pretty sure about this, not dynamic since he isn’t running the malware. Agree?
2
B is what I'd pick, since ResourcesExtract pulls out strings and readable data from executables during static analysis. It's not really mapping dependencies, more just extracting info you can scan for IOCs. Pretty sure about this, but if someone thinks A fits better let me know.
Q: 7
Jason discovered a file named $RIYG6VR.doc in the C:\$Recycle.Bin\\ while analyzing a hard disk image for the deleted dat a. What inferences can he make from the file name?
Options
35 comments in the community discussion
7
Option D
6
D . The $R at the start tells us it's a deleted file sitting in the Recycle Bin and the .doc extension means it's a Word doc. Windows generates that $R string, so it doesn't reflect the original filename. Pretty confident about D for what can be inferred here, unless I'm missing something.
Q: 8
A forensic examiner is examining a Windows system seized from a crime scene. During the examination of a suspect file, he discovered that the file is password protected. He tried guessing the password using the suspect’s available information but without any success. Which of the following tool can help the investigator to solve this issue?
Options
38 comments in the community discussion
1
Pretty sure A. Saw similar in recent exam report, Cain & Abel is for cracking passwords.
1
A tbh, since Recuva is tempting but really just for deleted files. Cain & Abel does password recovery, which matches this scenario. If anyone thinks C is right for password cracking, let me know!
Q: 9
Which of the following attacks allows an attacker to access restricted directories, including application source code, configuration and critical system files, and to execute commands outside of the web server’s root directory?
Options
34 comments in the community discussion
1
C vs D again but C fits best since it's asking for the specific attack not just a config issue.
1
C. pretty sure. Directory traversal is the one that lets attackers reach files outside web root like source code and configs.
Q: 10
Report writing is a crucial stage in the outcome of an investigation. Which information should not be included in the report section?
Options
41 comments in the community discussion
1
A , speculation or opinion is the trap here. Facts only in forensic reports, not personal takes.
1
Why would you put speculation or opinion (A) in a forensic report? Those just aren't allowed, pretty sure only facts and procedures go in. Anyone disagree?
Q: 11
Centralized binary logging is a process in which many websites write binary and unformatted log data to a single log file. What extension should the investigator look to find its log file?
Options
7 comments in the community discussion
1
B is wrong here, C fits since .ibl is actually used for centralized binary logs on IIS setups. .log would be standard for plain text, but this one's definitely asking about the binary format. Seen similar wording before. If anyone's seen it differently let me know, but I'm pretty sure about C.
B tbh
Q: 12
When performing a forensics analysis, what device is used to prevent the system from recording data on an evidence disk?
Options
5 comments in the community discussion
1
A for sure, write-blocker literally exists to stop any changes on the evidence disk. Keeps chain of custody clean and protects data integrity. Don't see how the others fit here honestly.
A imo, since a write-blocker is standard practice in forensics. It stops anything from changing evidence disks during analysis which keeps it admissible. The other options don’t actually prevent writes. Pretty sure about this, but open if someone has seen otherwise.
Q: 13
Where should the investigator look for the Edge browser’s browsing records, including history, cache, and cookies?
Options
6 comments in the community discussion
1
Had something like this in a mock and I picked B, thinking browser artifacts might spill to virtual memory during active sessions. For full history though, maybe that’s not the best place-still, isn’t some session data kept there? Let me know if I’m off.
Totally ESE Database for this one. A
Q: 14
What is the capacity of Recycle bin in a system running on Windows Vista?
Options
10 comments in the community discussion
5
D . Windows Vista by default uses 10% of each partition for the Recycle Bin, unless someone customizes it.
1
Its C for me, since I've seen similar questions in official prep guides saying users can set the size and sometimes it feels unlimited on big drives. Not 100% sure though, maybe check the official docs or labs to confirm.
Q: 15
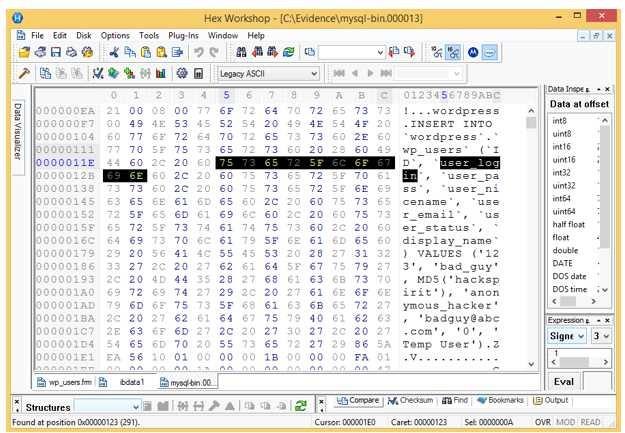
Analyze the hex representation of mysql-bin.000013 file in the screenshot below. Which of the following will be an inference from this analysis? ECcouncil CHFI 312-49v10 question
Options
8 comments in the community discussion
6
Option D had something just like this in a mock exam. INSERT with 'bad_guy' really only fits new user creation.
2
D , the hex shows INSERT for 'bad_guy' so new user made.
Q: 16
Select the tool appropriate for finding the dynamically linked lists of an application or malware.
Options
10 comments in the community discussion
2
Nope, for finding DLL dependencies you'd pick D here. PEiD is more about packers and signatures.
1
D , encountered exactly similar question in my exam and Dependency Walker was correct.
Q: 17
To check for POP3 traffic using Ethereal, what port should an investigator search by?
Options
7 comments in the community discussion
1
Its D
C or D? I remember seeing POP3 on port 125 in some older setups, so maybe D is right here. Not totally sure though since C also looks familiar.
Q: 18
John is working on his company policies and guidelines. The section he is currently working on covers company documents; how they should be handled, stored, and eventually destroyed. John is concerned about the process whereby outdated documents are destroyed. What type of shredder should John write in the guidelines to be used when destroying documents?
Options
6 comments in the community discussion
1
B tbh
C or DI remember seeing criss-cross as a secure option in some guides, so I think D could be right. Strip-cut is too basic, and cross-hatch sounds unusual. Not 100% sure though, maybe I'm falling for a trap option.
Q: 19
If you discover a criminal act while investigating a corporate policy abuse, it becomes a publicsector investigation and should be referred to law enforcement?
Options
8 comments in the community discussion
5
True imo. Once it's a criminal act, the private investigation hands it off to law enforcement for public sector handling.
5
Guessing True here. If it’s a criminal act, law enforcement gets involved right away.
Q: 20
Rule 1002 of Federal Rules of Evidence (US) talks about
Options
13 comments in the community discussion
2
Option A, had something like this in a mock and picked it for admissibility reasons.
1
A tbh, since I remember seeing similar questions in other guides where Rule 1002 was linked to admissibility more broadly, not just the 'requirement'. Some practice tests kinda blur that line. But honestly, probably C is stricter by the letter of the law. If anyone's prepped mainly with official materials, let me kn
Question 1 of 20

Premium Access Includes

  • Quiz Simulator
  • Exam Mode
  • Progress Tracking
  • Question Saving
  • Flash Cards
  • Drag & Drops
  • 3 Months Access
  • PDF Downloads
Get Premium Access
Scroll to Top